
Advisories
Iranian Targeted Malware Campaign: CHOSEN BRICK Exploits Dissidents, Activists, and Journalists
The National Cyber Security Centre (NCSC) has identified a new Iranian‑originated malware family, CHOSEN BRICK, that is specifically targeting dissidents, activists and journalists. The malware is delivered via spear‑phishing emails and exploits a Windows credential‑dumping tool to gain persistence. Defenders should block the associated domains, update endpoint protection, and enforce multi‑factor authentication for all users.
What happened
The National Cyber Security Centre (NCSC) has reported a new Iranian‑originated malware family, CHOSEN BRICK, that is actively targeting dissidents, activists and journalists.
Targeted groups
Campaign focuses on individuals who publicly criticize the Iranian government, including political dissidents, human rights activists and investigative journalists.
Technical overview
Delivery occurs via spear‑phishing emails containing a malicious attachment. Once executed, the malware uses a credential‑dumping tool to harvest Windows credentials, then establishes persistence through scheduled tasks and writes a backdoor DLL to the system32 folder. It communicates with a command‑and‑control server over HTTPS using a custom TLS‑based protocol.
Mitigations
- Block all known CHOSEN BRICK domains and IP addresses listed in the NCSC advisory.
- Ensure endpoint protection is up to date and enable real‑time scanning.
- Enforce multi‑factor authentication for all accounts, especially those with privileged access.
- Disable execution of unsigned PowerShell scripts and enforce application whitelisting.
- Monitor for credential‑dumping tools (e.g., Mimikatz) and scheduled task creation on endpoints.
Related vulnerabilities
HEAVYGRAM Surveillance Backdoor Leverages Telegram C2 and Targets Iranian Dissidents
Security researchers have detailed HEAVYGRAM, a Windows surveillance backdoor active since late 2023 and linked with moderate confidence to the Iran-aligned threat group Handala Hack. The malware utilizes Telegram's infrastructure for command-and-control operations to target journalists, dissidents, and government opponents.
Read briefing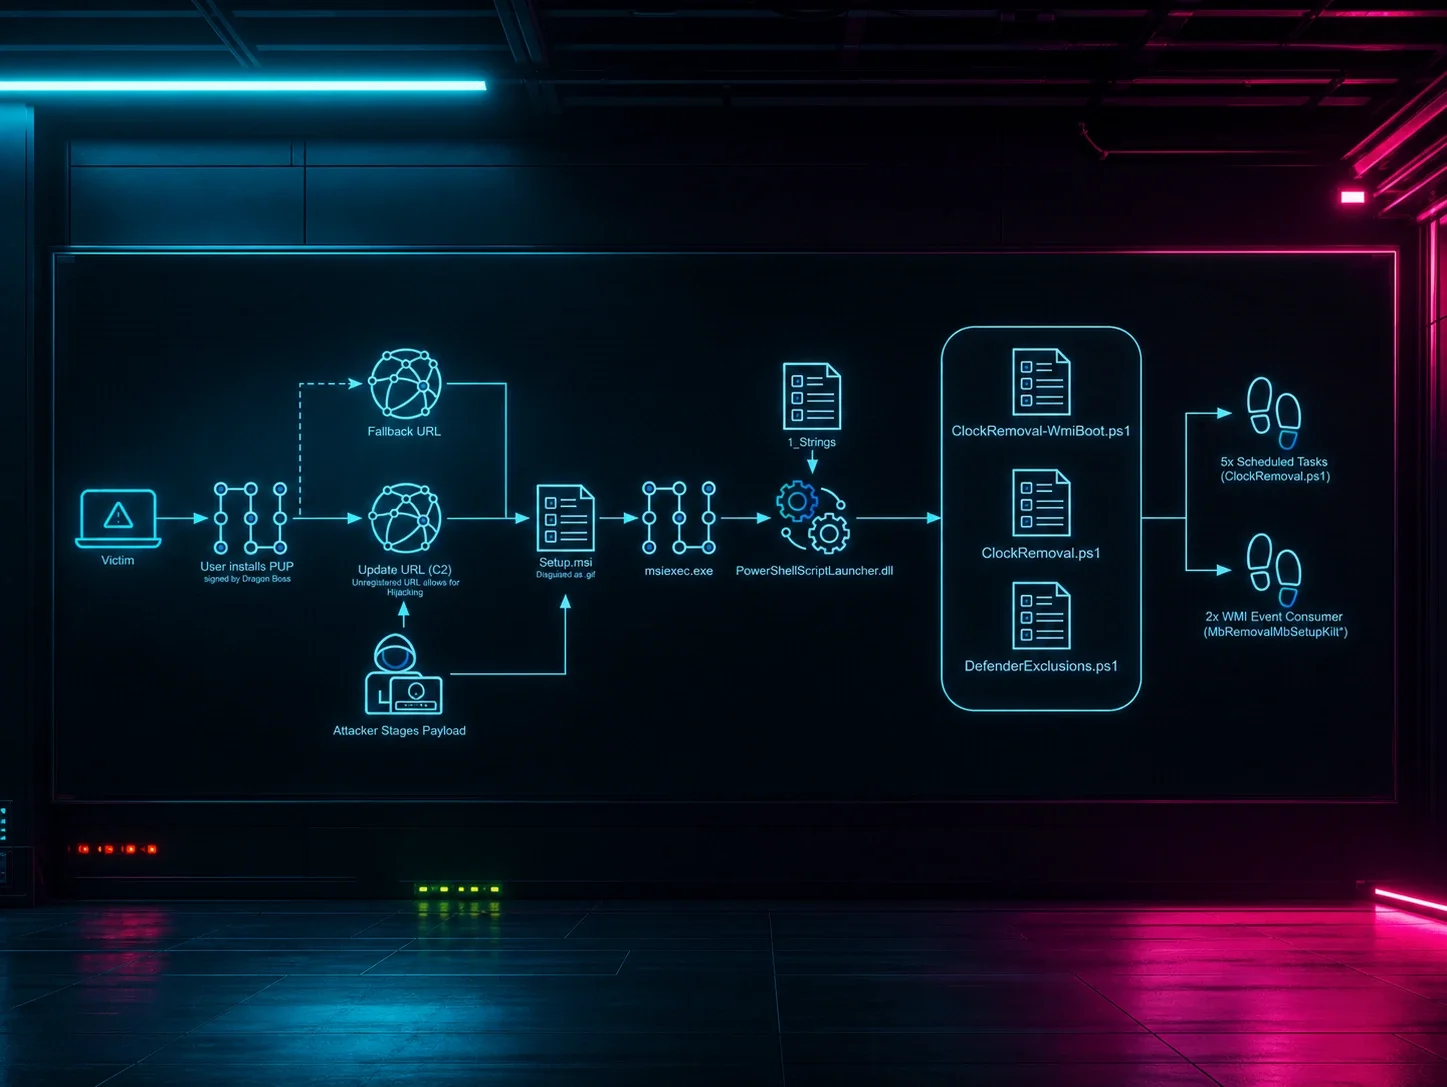
Signed PUP Exploits Update Mechanism to Deploy AV Killers with SYSTEM Privileges
Huntress identified a malware campaign that leverages a signed potentially unwanted program (PUP) to install antivirus‑killers with SYSTEM rights. The operation abuses the software’s update channel, allowing attackers to gain full control over endpoints. Defenders should audit signed binaries, monitor privileged process creation, and enforce least‑privilege update mechanisms.
Read briefing
TONResolver RAT Targets Japanese Hospitality Sector via Booking.com Phishing
A targeted phishing campaign observed in May 2026 deployed the TONResolver RAT against hotels and accommodation providers in Japan. Threat actors utilized Booking.com-themed lures to deliver the malware, which uniquely abuses the TON blockchain for command-and-control operations.
Read briefing
Operation Bleeding Bear: MBR‑Wiping Malware Targeting Ukrainian Entities
A multi‑stage destructive campaign, Operation Bleeding Bear, targeted Ukrainian government and private organizations in January 2022. The malware overwrites the Master Boot Record and corrupts critical files without demanding ransom. Defenders should enable Elastic Security’s EDR and Ransomware Protection modules and monitor for MBR write attempts.
Read briefing