
Threat Intel
HEAVYGRAM Surveillance Backdoor Leverages Telegram C2 and Targets Iranian Dissidents
Security researchers have detailed HEAVYGRAM, a Windows surveillance backdoor active since late 2023 and linked with moderate confidence to the Iran-aligned threat group Handala Hack. The malware utilizes Telegram's infrastructure for command-and-control operations to target journalists, dissidents, and government opponents.
What Happened
Threat intelligence analysts have published technical details regarding HEAVYGRAM, a bespoke Windows backdoor active since Autumn 2023. Attributed with moderate confidence to the threat actor known as Handala Hack, the tool is primarily designed for targeted surveillance against specific demographics, including Iranian dissidents, journalists, and perceived government opponents.
Technical Mechanics and C2
Unlike traditional malware utilizing custom infrastructure, HEAVYGRAM leverages the Telegram messaging platform as its command-and-control (C2) channel. This abuse of legitimate API services complicates network-level detection since traffic blends in with standard messaging application usage. Key operational capabilities include:
- Remote command execution on compromised Windows systems
- Data exfiltration routed through Telegram infrastructure
- Persistence mechanisms to survive system reboots
- Targeted reconnaissance tailored for espionage operations
Attribution and Targeting
The campaign's targeting profile focuses heavily on individuals and entities of interest to Iranian state-aligned actors. Handala Hack has previously deployed various tooling, but the operational reliance on HEAVYGRAM highlights an ongoing trend of threat actors adopting abused cloud and messaging platforms to minimize hosting costs and evade traditional perimeter blocklists.
What Defenders Should Do
Security operations centers and system administrators should review telemetry and endpoint behavior associated with unauthorized Telegram API usage or unexpected script execution spawned from messaging applications. Recommendations include:
- Monitor for unauthorized or anomalous outbound connections to Telegram endpoints from sensitive workstations.
- Audit endpoint detection and response (EDR) rules for suspicious process ancestry involving living-off-the-land binaries executing following file drops.
- Implement strict application control policies to prevent the execution of unverified binaries on high-risk endpoints.
Related articles
Iranian Targeted Malware Campaign: CHOSEN BRICK Exploits Dissidents, Activists, and Journalists
The National Cyber Security Centre (NCSC) has identified a new Iranian‑originated malware family, CHOSEN BRICK, that is specifically targeting dissidents, activists and journalists. The malware is delivered via spear‑phishing emails and exploits a Windows credential‑dumping tool to gain persistence. Defenders should block the associated domains, update endpoint protection, and enforce multi‑factor authentication for all users.
Read briefing
Chinese Espionage Group Deploys New SparroWocky Backdoor in Latin America
FamousSparrow, a China‑linked threat actor, has moved beyond its old SparrowDoor tool and rolled out the modular C++ backdoor SparroWocky against government entities across Latin America. The malware uses sophisticated anti‑analysis tricks—DLL side‑loading, RC4‑encoded payloads, dynamic API resolution, and CreateThread hooking—to evade detection. It can execute commands, exfiltrate data, capture high‑frequency screenshots, proxy traffic, and even wipe its own traces. ESET’s analysis pinpoints 18 C2 endpoints and shows the operation has been active for over a year, targeting Argentina, Ecuador,
Read briefing
Star Blizzard Shifts to RedFlick Phishing, Deploys CosmicPulse Backdoor
Star Blizzard, a Russia‑linked APT group, has moved from ClickFix to a new phishing technique called RedFlick, enabling delivery of the CosmicPulse backdoor with reduced user interaction. The change targets Ukrainian‑linked NGOs, think tanks, and journalists, increasing compromise likelihood and evasion of detection. Defenders should update email filters, deploy EDR signatures, and monitor for CosmicPulse indicators.
Read briefing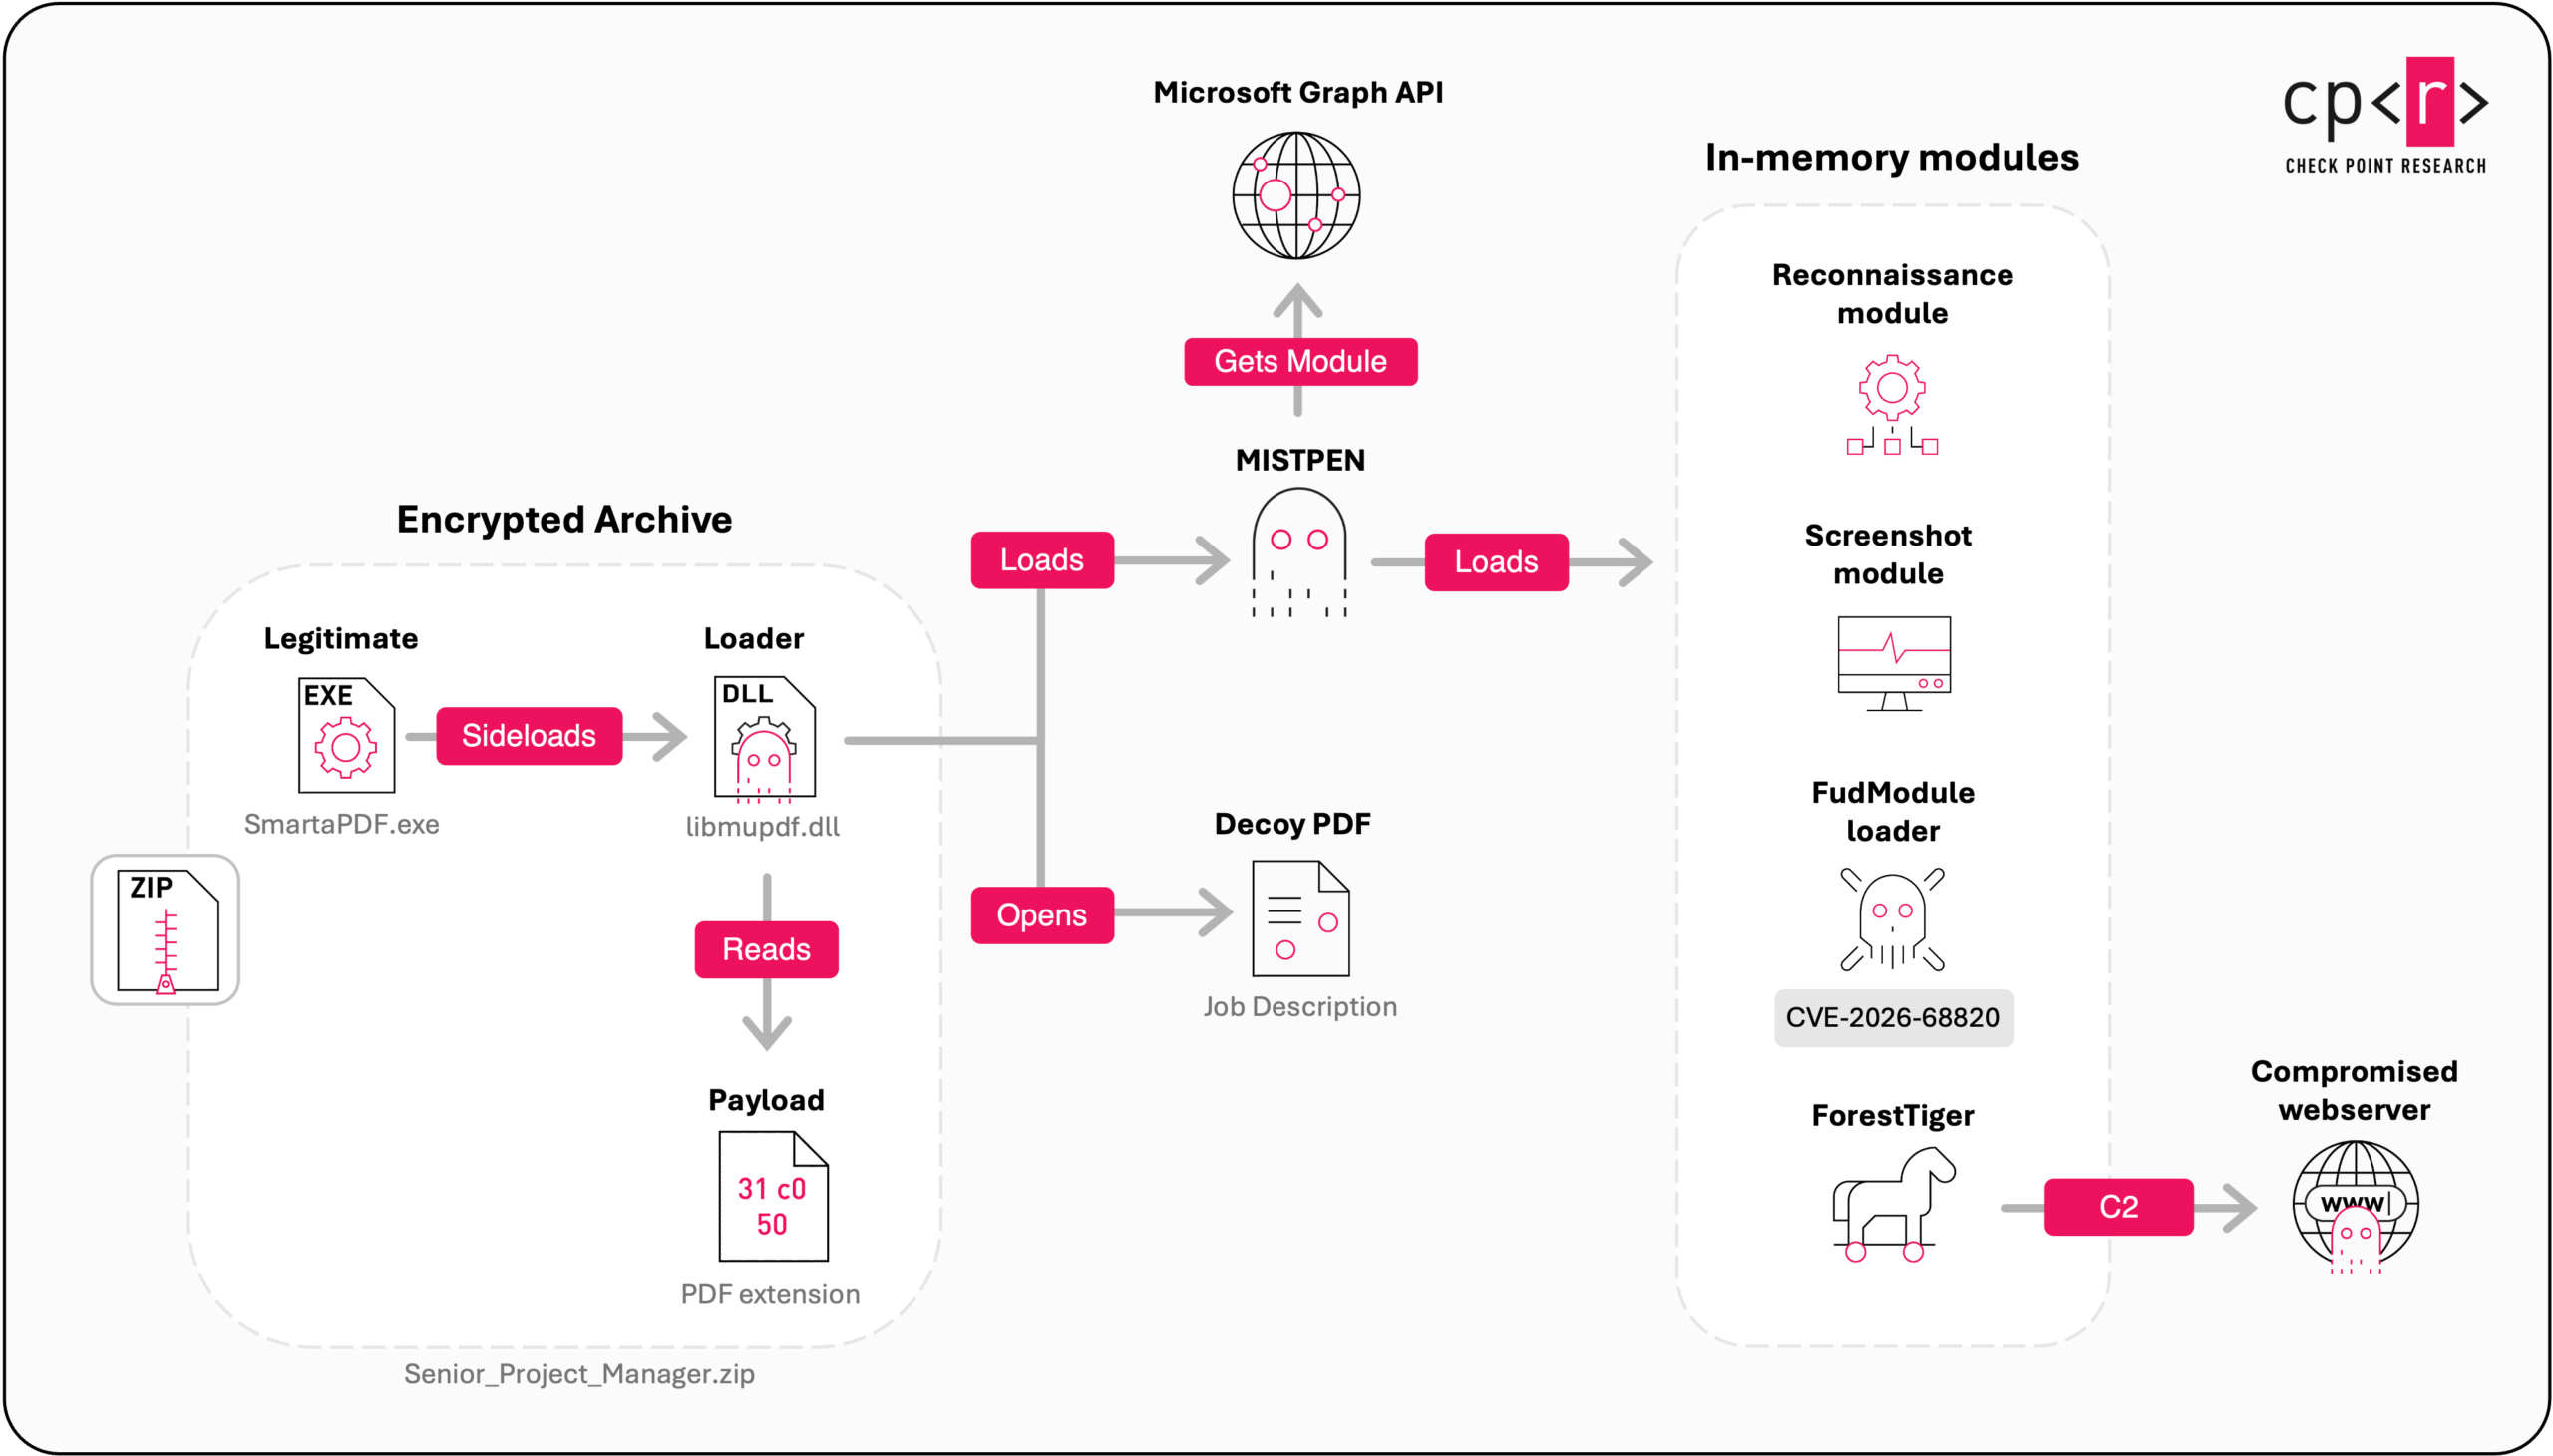
Operation Dream Job: From Job Offers to Zero‑Day Attacks on Defense Sectors
Check Point Research has traced a fresh wave of the Operation Dream Job campaign, a Lazarus‑linked effort that turns enticing job ads into a multi‑stage breach. The attackers now use a trojanized PDF viewer, the SecurityPDF app, to deliver a new kernel‑mode rootkit (FudModule) via the zero‑day CVE‑2026‑68820 in Microsoft’s AFD.sys driver. They also weaponize CVE‑2025‑49113 in Roundcube to plant RelayShell webshells, turning compromised servers into covert C2 relays. The campaign targets aerospace, aviation and defense firms worldwide, leveraging spear‑phishing, SEO‑boosted fake recruitment sit
Read briefing