
Threat Intel
Elastic Security Releases Free Cloud Detection Rules for AWS and Okta
Elastic Security’s Intelligence & Analytics team has released a set of free detection rules for AWS and Okta, added in version 7.9. The rules help defenders surface suspicious cloud activity with minimal configuration. Deploying them improves detection coverage for cloud‑centric attacks.
What Happened
Elastic Security’s Intelligence & Analytics team has published a set of free detection rules that target attacker activity in cloud environments, specifically AWS and Okta. The rules were added to Elastic Security 7.9 and are available to all users without cost.
Impact
Organizations that have migrated workloads to AWS or use Okta for identity management now have a ready‑made rule set that can surface suspicious API calls, privilege escalations, and anomalous sign‑ins. Defenders who rely on SIEM ingestion of cloud logs will see higher detection coverage with minimal tuning.
What to Do
- Enable the new rules in your Elastic Security deployment and verify that the corresponding log types (AWS CloudTrail, Okta logs) are being ingested.
- Map the logs to the Elastic Common Schema (ECS) to ensure field names are consistent across sources.
- Review the rule documentation for required fields and adjust any custom thresholds that fit your environment.
- Set up alerts or dashboards that surface rule hits in real time, and incorporate them into your incident‑response playbooks.
Next Steps
Elastic Security continues to expand its rule catalog and will add support for additional cloud platforms in upcoming releases. Stay tuned to the Elastic blog for updates.
Related articles
Dorothy Enables Okta Visibility Testing for SecOps Teams
Security teams can now validate their Okta SSO monitoring with Dorothy, a free open‑source tool that simulates attacker actions and maps them to MITRE ATT&CK tactics. By running Dorothy tests and leveraging Elastic Security’s detection rules, defenders can confirm that logs, alerts, and response playbooks cover the most common IAM attack vectors.
Read briefing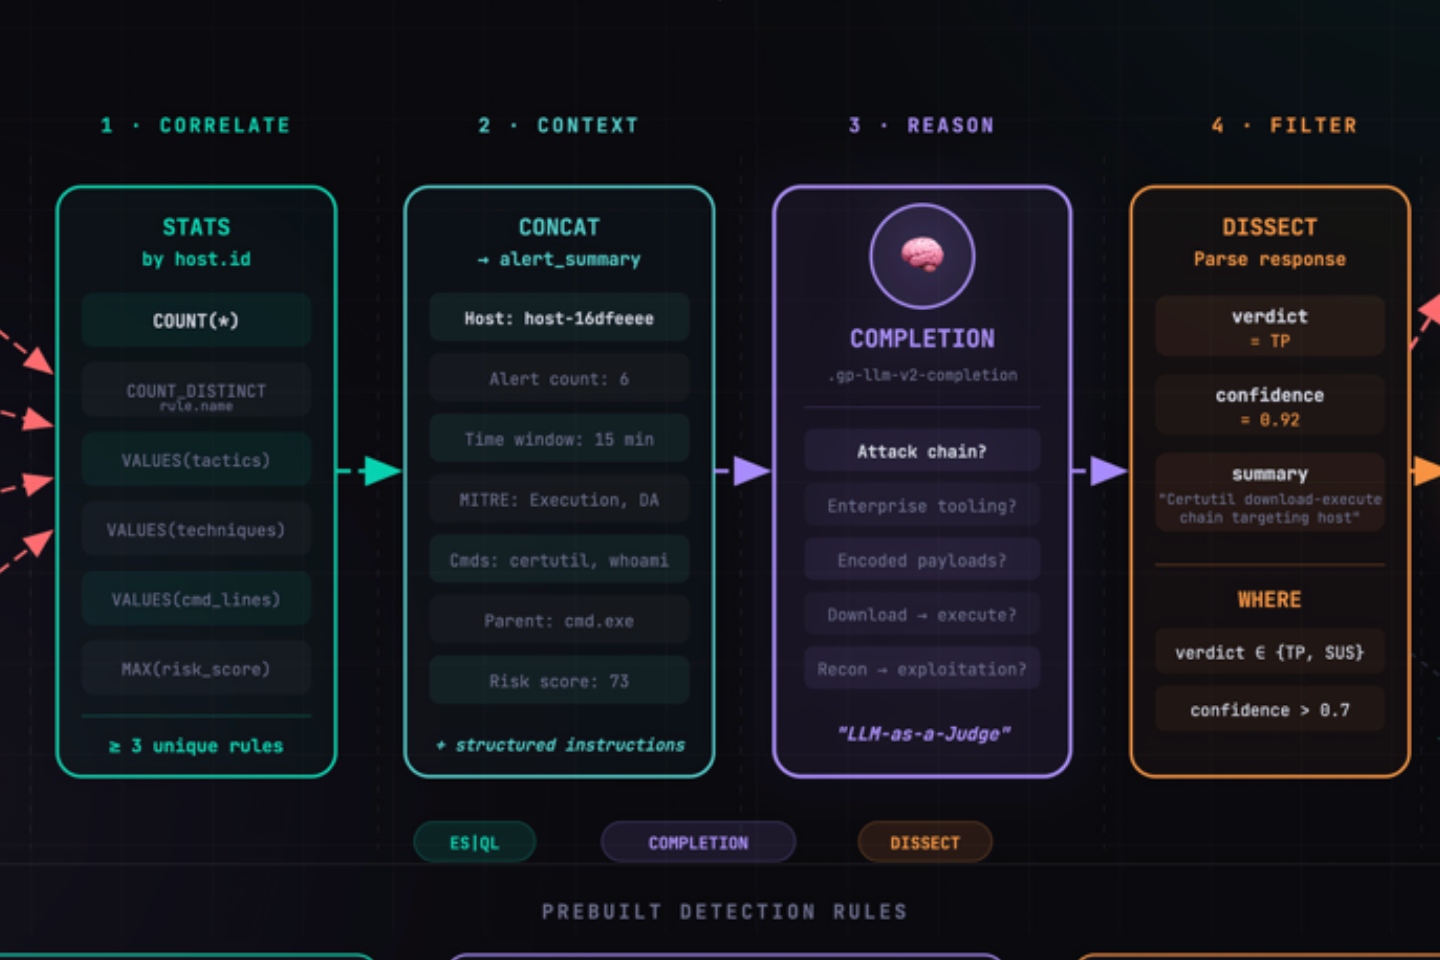
Elastic ES|QL COMPLETION Enables In‑Query LLM Reasoning for Detection Triage
Elastic has added the COMPLETION command to ES|QL, allowing detection engineers to embed LLM inference directly into query logic. This eliminates the need for external SOAR or scripts to add contextual reasoning to behavioral rules. Defenders can now build smarter alert triage within a single query, using Elastic Cloud models or external LLM connectors.
Read briefing
Elastic Security 9.3 Adds Tech‑Preview QRadar Rule Migration
Elastic Security 9.3 introduces a tech‑preview Automatic Migration for QRadar detection rules, allowing SecOps teams to translate Event, Flow, and Common rules—including reference sets and MITRE mappings—into Elastic‑native logic. Defenders can choose rule‑first or data‑first onboarding and verify integrations before production.
Read briefing
Advanced Linux Persistence Detection: New Guidance on Init Scripts and Custom Tools
Elastic Security’s latest Linux persistence series expands beyond Systemd to cover System V and Upstart init scripts, and introduces PANIX for testing persistence. Defenders can now deploy pre‑built detection rules, audit critical init directories, and validate coverage with the new tool.
Read briefing