
Malware
GoldPickaxe iOS Trojan: Face‑ID Stealer and How to Detect It
GoldPickaxe is a new iOS Trojan that harvests Face‑ID data and exfiltrates it to remote servers. The malware targets iOS 14+ devices, exploiting a flaw in the biometric framework. Defenders should enforce strict app vetting, monitor for unauthorized biometric usage, and keep devices updated.
GoldPickaxe is a newly identified iOS Trojan that captures Face‑ID biometric data and sends it to a command‑and‑control server. The malware was discovered in a sample that ran on iOS 14 and later, using a zero‑day vulnerability in the system’s biometric API to bypass user consent. The threat is classified as high severity due to the sensitive nature of the data exfiltrated.
Impact
Devices infected with GoldPickaxe lose the integrity of their biometric authentication. The stolen Face‑ID templates can be used for spoofing or to bypass authentication on other Apple services. Users who have enabled Face‑ID for unlocking, Apple Pay, or iCloud Keychain are at risk.
Detection
- Look for unfamiliar apps that request biometric permissions without a clear purpose.
- Monitor network traffic for outbound connections to suspicious domains or IP ranges associated with the Trojan.
- Use device management logs to detect repeated biometric API calls from a single app.
Mitigation
- Keep iOS and all installed apps updated to the latest releases.
- Enforce a strict App Store policy; block sideloaded or enterprise‑distributed apps that are not vetted.
- Configure MDM to revoke biometric permissions for apps that do not require them.
- Deploy mobile threat defense solutions that can detect anomalous biometric usage.
What to Do
Security teams should immediately audit all devices for the presence of GoldPickaxe, revoke any unauthorized biometric permissions, and reset Face‑ID templates on affected devices. Consider implementing a zero‑trust approach to biometric data, requiring re‑enrollment after any security incident.
Related articles
P7 DarkSword iOS Exploit Kit Adds Keychain Theft and Remote Command Capability
A new P7 variant of the DarkSword iOS exploit kit has been identified, featuring a smaller on‑device footprint, on‑device keychain and crypto‑wallet theft, and two‑way command and control. The kit targets iOS 18.4–18.7 and has been used in campaigns across Saudi Arabia, Turkey, Malaysia, Ukraine, and by a Chinese‑speaking actor. Defenders should update iOS, enforce app‑whitelisting, and monitor for suspicious network traffic to mitigate the threat.
Read briefing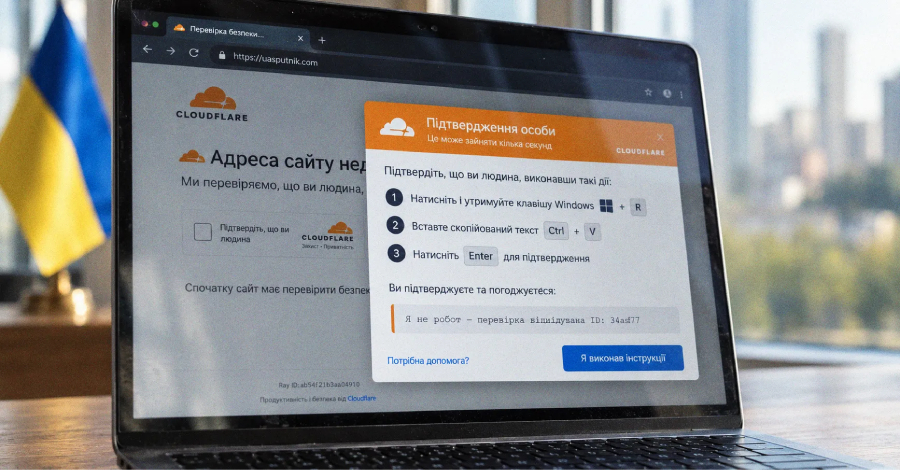
ClickFix Campaign Compromises Ukrainian Sites, Deploys Psychedelic Stealer via Fake Cloudflare Verification
An active ClickFix campaign has injected fake Cloudflare verification pages into legitimate Ukrainian business sites, tricking visitors into running an MSI installer that delivers the Psychedelic stealer. The malware harvests credentials, cryptocurrency wallet data, and establishes persistence via scheduled tasks. Defenders should block the attacker domains, detect MSI executions, and harden web applications against iframe injection.
Read briefing
Hirudo Android Malware Hijacks Banking Apps to Steal Credentials
Hirudo is an Android malware that replaces legitimate banking apps with malicious copies, disabling security checks to harvest credentials and remotely control devices. It targets banks in Indonesia, China, India, Mexico, Morocco, and Thailand, and is delivered via apps that masquerade as shopping or entertainment services. Defenders should verify app signatures, enforce Play Integrity, restrict Accessibility permissions, and deploy mobile security solutions to detect hooking engines.
Read briefing
RTM Group Banking Trojan Infection: Forensic Findings and Defender Actions
A forensic investigation of a workstation infected with a banking trojan distributed by the RTM group revealed credential theft, persistence, and lateral movement. Defenders should isolate affected hosts, review authentication logs, and deploy EDR signatures to mitigate future attacks.
Read briefing