
Advisories
Google Fined €403M by Ireland’s DPC Over GDPR Violations in Location Data Handling
Google was fined €403 million by Ireland’s Data Protection Commission for unlawful processing of location data in Web & App Activity, Location History, and Location Accuracy from May 2018 to February 2020. The DPC ordered the company to bring its practices into compliance within six months. Defenders should audit their own location‑data workflows for lawful basis, transparency, and retention limits.
Google has been fined €403 million by Ireland’s Data Protection Commission (DPC) for violating the EU General Data Protection Regulation (GDPR) in the way it processed users’ location data between May 2018 and February 2020. The penalty covers three Google features: Web & App Activity, Location History, and Location Accuracy.
Impact
The DPC found that Google failed to provide lawful, fair, and transparent processing of location data, and that it retained such data longer than necessary. Users could have been unaware that their movements were tracked and used for advertising or profiling, and they lost control over their personal information.
What Defenders Should Do
Review any systems that collect, store, or analyze location data. Confirm that a lawful basis exists, that users are clearly informed, and that retention periods are limited to what is strictly required for the stated purpose.
Key Compliance Actions
- Document the lawful basis for each location‑data processing activity.
- Implement clear opt‑in/opt‑out mechanisms and provide concise privacy notices.
- Set automated deletion or anonymisation schedules that align with the minimal‑retention principle.
- Conduct regular audits to verify that location data is not processed beyond the agreed scope.
“These failures meant people could have been unaware that their location was being used, for example, to influence them with ads or to infer their interests,” said DPC Deputy Commissioner Graham Doyle.
Related articles
Google Fined €403 Million by Irish DPC Over Misleading Location Tracking Controls
Ireland's Data Protection Commission has penalized Google €403 million following a six-year investigation into how user location data was gathered and utilized between 2018 and 2020. The inquiry revealed that disabling the Location History setting failed to halt telemetry collection through separate configurations like Web & App Activity.
Read briefing
IQVIA Fined €7M for Inadequate Health‑Data Anonymization in Italy
The Italian Data Protection Authority imposed a €7 million fine on IQVIA after discovering that the company’s Italian division had stored a database of about one million patients with insufficient anonymization, enabling potential re‑identification. The incident highlights the need for robust de‑identification practices when handling health data.
Read briefing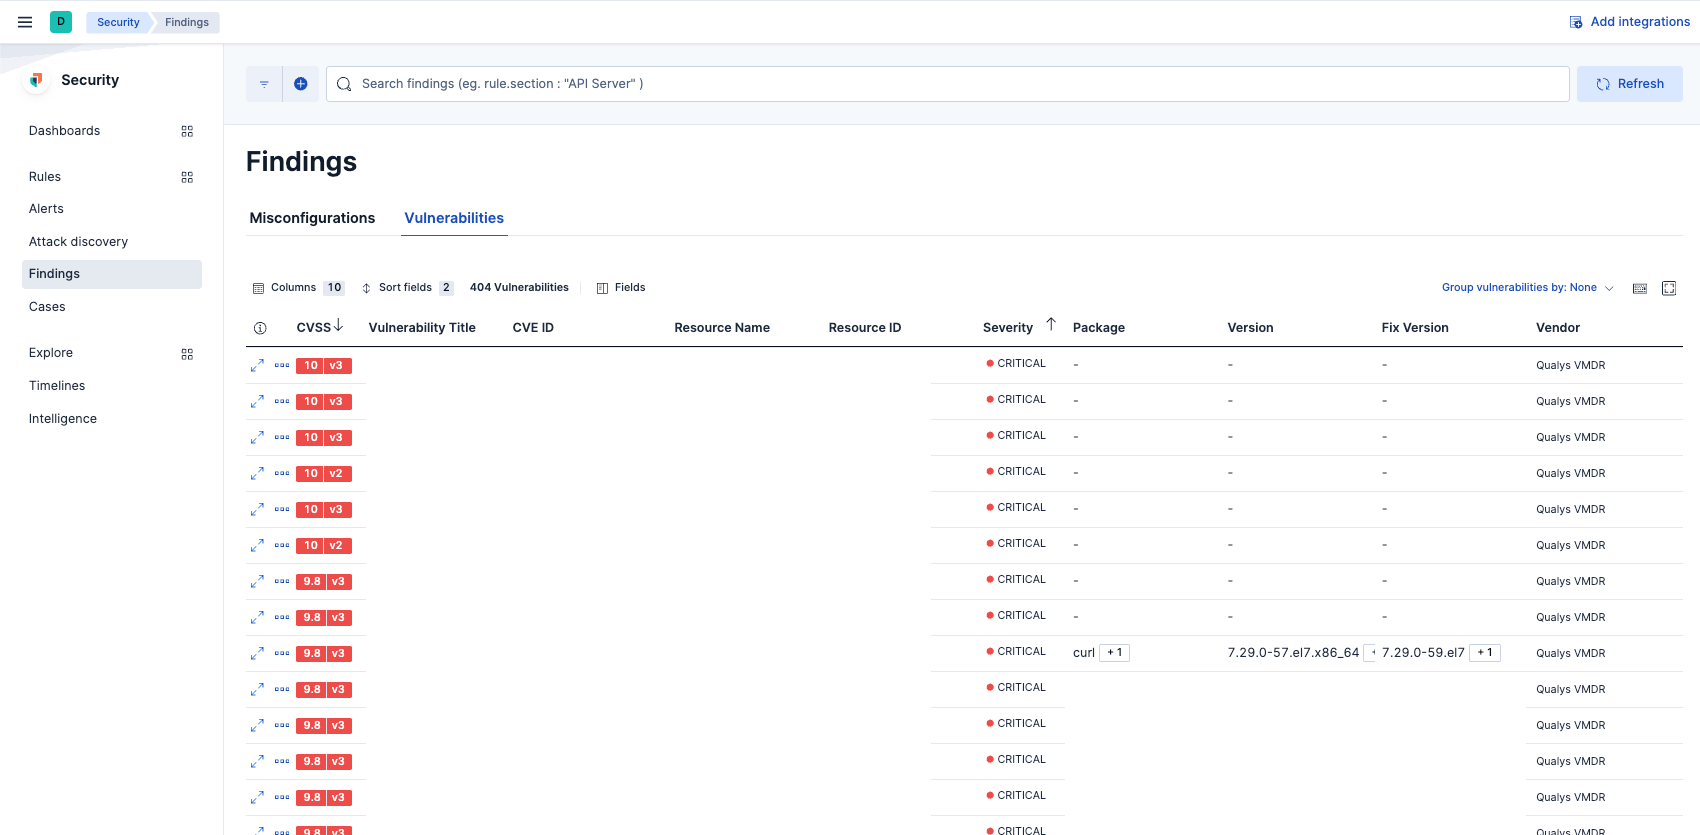
Using Survival Analysis to Measure Patch Velocity in Qualys VMDR with Elastic Stack
Survival analysis offers a more accurate view of vulnerability remediation than MTTR by accounting for censored data. By applying it to Qualys VMDR data in Elastic, defenders can quantify patching probability over time, benchmark teams, and pinpoint bottlenecks. This briefing explains the approach and actionable steps.
Read briefing
Mass Scans Target Exposed Vite Development Servers for Cloud Secrets
A new wave of attackers is hunting internet‑exposed Vite dev servers for AWS and Azure credentials, using the recently disclosed CVE‑2026‑39364 to bypass file‑access controls. Over 800 attacks were logged by F5, with attackers leveraging Google Cloud IP ranges and exploiting additional Vite CVEs. The campaign focuses on .env files, AWS config, Terraform state, and serverless configs. RootPwn recommends updating Vite to 8.0.5 or later, blocking port 5173, filtering /@fs/ requests, and rotating any secrets exposed by vulnerable instances.
Read briefing