
Advisories
Microsoft Patch Tuesday October 2026: 85 Critical Vulnerabilities, 1 Wildly Exploited RCE
Microsoft’s October 2026 update addresses 1,415 flaws, including 85 critical ones. A wild‑exploited Windows Shell command‑injection (CVE‑2026‑96951) and multiple high‑impact RCEs in AD DS, Exchange, Message Queuing, Office, and Hyper‑V are highlighted.
What Happened
Microsoft released its October 2026 security update, addressing 1,415 vulnerabilities, 85 of which are marked critical. The update includes a wild‑exploited Windows Shell command‑injection flaw (CVE‑2026‑96951) and several high‑impact RCEs in core services.
Impact
- CVE‑2026‑96951 – Windows Shell command injection, CVSS 8.8, exploited in the wild.
- CVE‑2026‑70229 – AD DS RCE, CVSS 8.1.
- CVE‑2026‑70571 – Exchange Server RCE, CVSS 8.1.
- CVE‑2026‑100202 – Message Queuing RCE, CVSS 9.8.
- Multiple Office Excel RCEs (CVE‑2026‑100209, ‑100210, ‑100211, ‑97739, ‑97745, ‑97755, ‑97759, ‑97765, ‑97778, ‑97741, ‑97742, ‑97753, ‑97756, ‑97758, ‑97761, ‑97767, ‑97776, ‑97780) – CVSS 8.8.
- Hyper‑V RCEs (CVE‑2026‑105733, ‑102214, ‑108399) – CVSS 8.8, 8.8, 7.2.
What to Do
- Apply the October 2026 update immediately; verify installation with Windows Update or WSUS.
- Prioritize patching Windows Shell, AD DS, Exchange, Message Queuing, Office, and Hyper‑V components.
- Deploy detection rules for known exploitation patterns (e.g., command‑injection payloads, RCE signatures).
- Monitor logs for anomalous activity such as unexpected shell execution or privileged escalation attempts.
- Validate that all endpoints, servers, and virtualized workloads are updated; consider temporary mitigations like disabling vulnerable features if patching is delayed.
Mitigation Notes
Microsoft recommends disabling the Windows Shell “RunAs” feature for untrusted users until the patch is applied, and applying the latest Exchange security baseline to mitigate CVE‑2026‑70571.
Related vulnerabilities
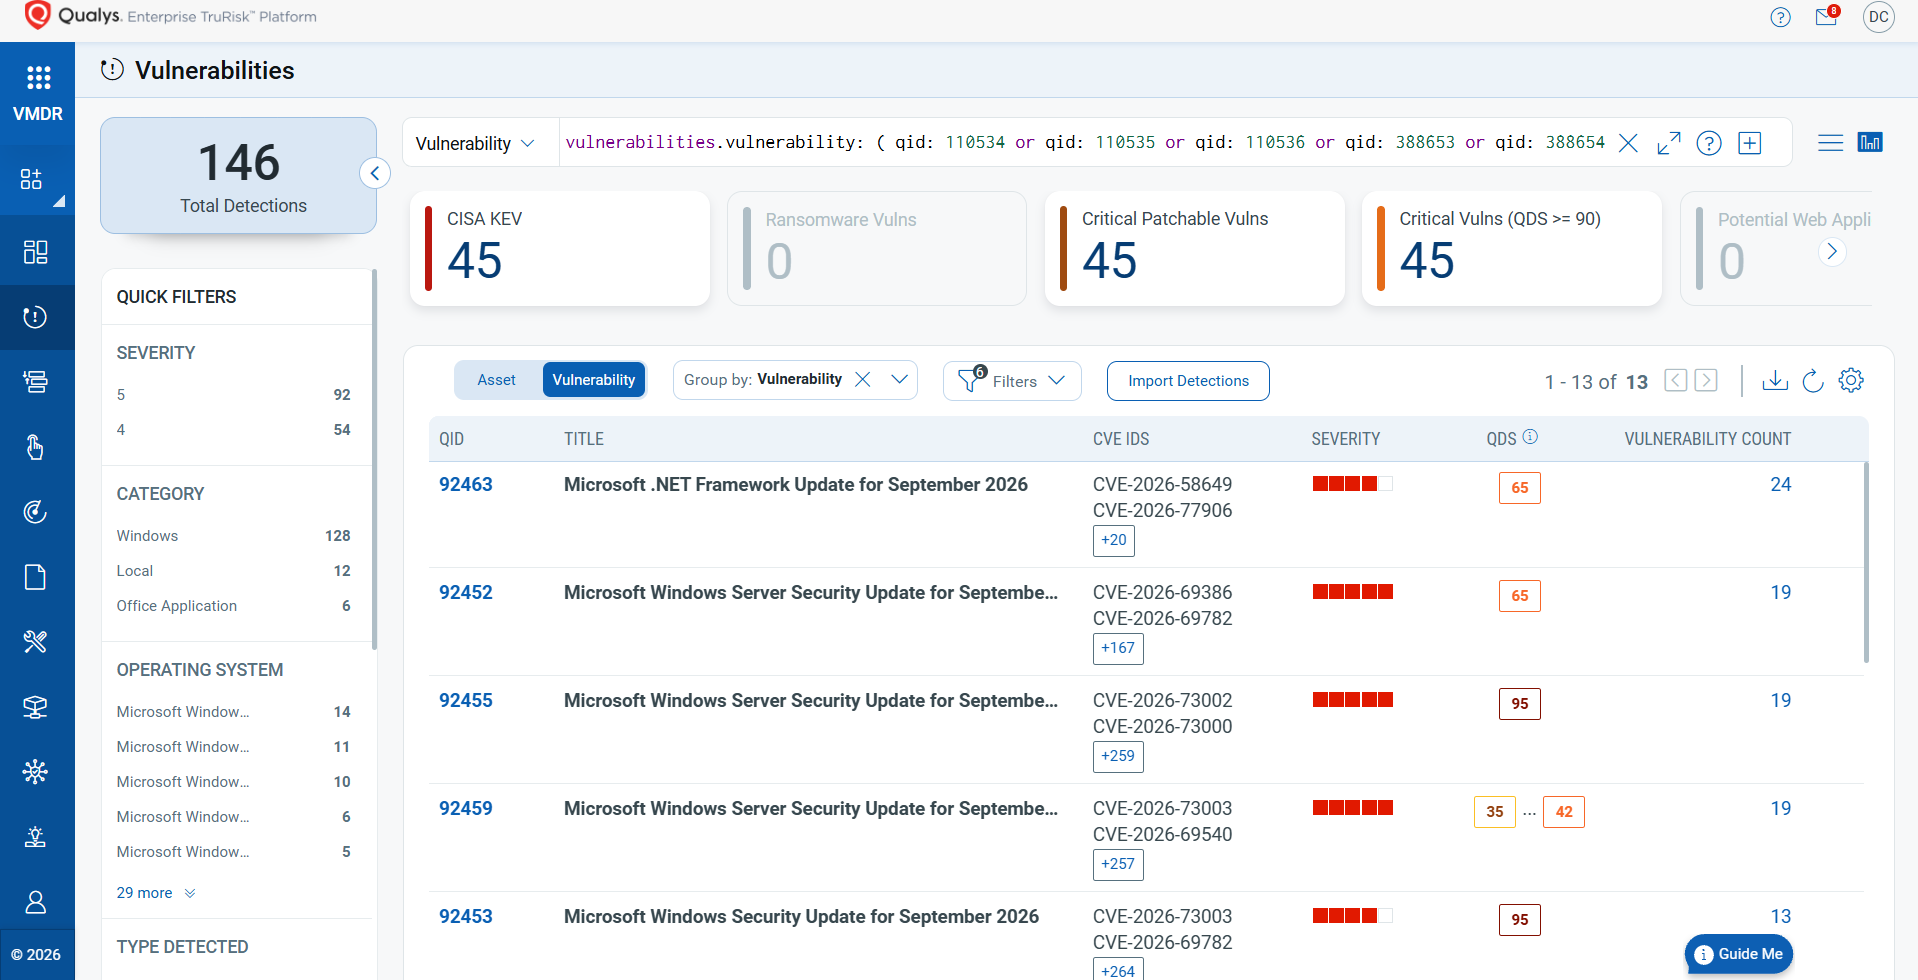
Microsoft September 2026 Patch Tuesday Addresses Record 974 Vulnerabilities
Microsoft's September 2026 Patch Tuesday marks its largest security update to date, addressing 974 vulnerabilities, including two actively exploited zero-days. Sysadmins and SecOps teams must prioritize the deployment of fixes covering critical components like Hyper-V, Windows HTTP.sys, and Exchange Server. Additionally, Adobe released advisories covering 170 vulnerabilities across its product ecosystem.
Read briefing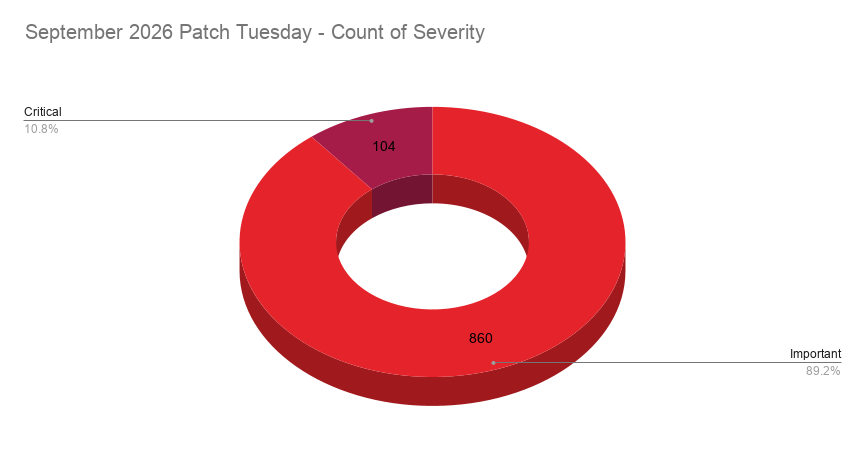
Microsoft September 2026 Patch Tuesday: 964 CVEs, Including Two Zero-Day Exploits (CVE-2026-81963, CVE-2026-85880)
Microsoft released its largest Patch Tuesday to date, addressing 964 CVEs—104 critical and 860 important—including two zero‑day vulnerabilities exploited in the wild. Defenders must prioritize applying updates to affected components such as .NET, Active Directory services, Azure services, Office, and Windows kernel drivers, and verify system integrity.
Read briefing
Microsoft Unleashes 972 CVE Fixes on Patch Tuesday, Including 2 Exploited Zero‑Days and 113 Critical Flaws
Microsoft’s September 2026 Patch Tuesday update tackles 972 CVEs—two of which are actively exploited zero‑days and 113 critical vulnerabilities. The patch covers Windows, Office, and other Microsoft components, tightening defenses across the ecosystem. Security teams should apply the fixes immediately and monitor for any lingering exploitation attempts.
Read briefing
Microsoft: SharePoint RCE CVE-2026-108452 was fixed in October 2026 updates but omitted from the update list
Microsoft clarified that CVE-2026-108452, a remote code execution vulnerability in Microsoft Office SharePoint, was fixed in October 2026 updates but was accidentally omitted from the published Security Updates list. The change is informational only. Defenders should verify that SharePoint systems have the October 2026 updates installed and no additional patching is required for those already patched.
Read briefing