
Advisories
NIST Releases Draft OT Security Guide Revision 4 and CISA Warns on ICS Integrator Risks
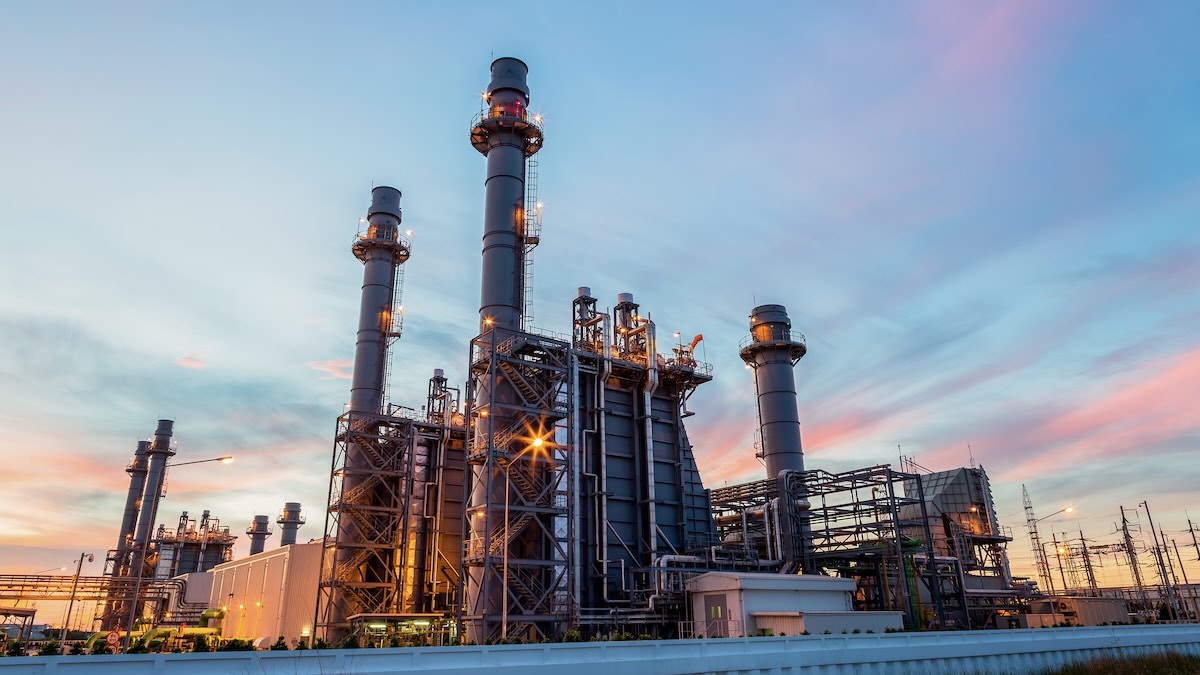
NIST has published draft Special Publication 800-82 Revision 4 for public comment, expanding operational technology security guidance across multiple critical infrastructure sectors and aligning with the NIST Cybersecurity Framework 2.0. Concurrently, CISA and the FBI issued advisory guidance concerning supply chain risks associated with third-party industrial control system (ICS) integrators.
What Happened
NIST released Revision 4 of Special Publication 800-82, titled Guide to Operational Technology (OT) Security, opening a public comment period that runs through November 30, 2026. Simultaneously, CISA and the FBI published a joint advisory highlighting security risks and threat vectors introduced by third-party industrial control system (ICS) integrators.
Key Updates and Scope
The updated NIST publication expands its sector-specific coverage to address modern industrial convergence and specialized environments. Key additions include:
- Inclusion of building automation, water and wastewater facilities, food and agriculture, freight rail, and maritime vessels.
- Guidance addressing the integration of industrial Internet of Things (IIoT) devices and cloud environments.
- Structural alignment with the NIST Cybersecurity Framework (CSF) 2.0, notably reorganizing legacy risk management content around the 'Govern' function.
- Expanded tactical frameworks for deploying OT security controls, prioritizing asset discovery and continuous network monitoring.
Defensive Action Items
SecOps and infrastructure defenders managing OT, SCADA, or ICS environments should review the draft documentation and assess current integration practices against federal guidance.
- Review NIST SP 800-82 Rev. 4 draft requirements and submit operational feedback prior to the November 30, 2026 deadline.
- Audit third-party ICS integrators for access controls, least-privilege enforcement, and secure remote maintenance channels.
- Implement or enhance passive asset discovery and network monitoring tailored to industrial protocols to identify unauthorized modifications or shadow IoT/cloud deployments.
Related articles
Meta Faces $25B Fine in New Mexico Privacy Ruling: Implications for Defenders
New Mexico court reduced Meta's initial $220B fine to $25B for 43 million unfair practice violations tied to the Cambridge Analytica scandal. The ruling underscores the need for robust data privacy compliance and transparent user data handling. Defenders should audit data flows, enforce access controls, and review third‑party integrations.
Read briefing
CrowdStrike Achieves NCSC CIR Enhanced Level Assurance: Implications for SecOps Teams
CrowdStrike Falcon has earned the UK government’s highest incident response assurance, the NCSC CIR Enhanced Level. This milestone signals stronger compliance, tighter security controls, and higher confidence for organizations deploying Falcon. SecOps teams should review configuration, validate policies, and monitor for any changes in the assurance framework.
Read briefing
Shift to Continuous Compliance: Mitigating Control Drift in AI-Driven Threat Landscapes
Traditional periodic compliance audits fail to address daily cloud infrastructure changes and AI-driven threats. Defenders must adopt continuous monitoring and automated evidence collection to bridge the gap between static assessments and real-world risk.
Read briefing
European Commission Proposes EU KIDS Act to Enforce Strict Age Limits and Design Mandates for Social Platforms
The European Commission has introduced the EU KIDS Act, a legislative proposal aimed at banning social media accounts for children under 13 and setting a bloc-wide minimum age of 15. The framework mandates strict safety-by-design standards, parental controls, and restrictions on addictive product features for minors across digital platforms.
Read briefing