
Advisories
Okta Breach by LAPSUS$ – Limited Access to End‑User Systems, Password Reset Capability
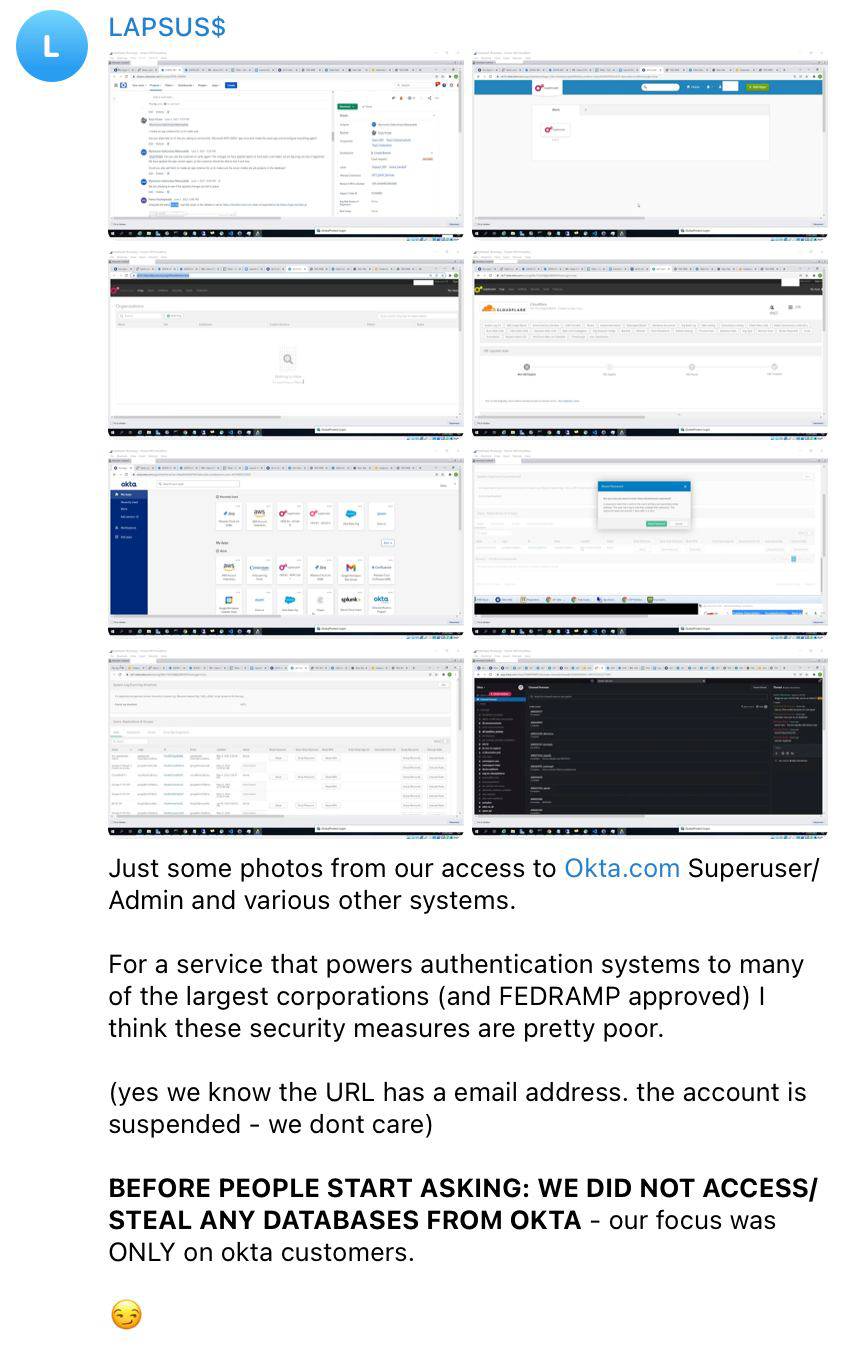
LAPSUS$ disclosed a January 2022 compromise of Okta that granted attackers access to a single end‑user workstation. The breach enabled password and MFA token resets but did not allow user creation, deletion, or data exfiltration. Defenders should audit reset logs, enforce MFA, and verify account integrity.
What Happened
In January 2022, LAPSUS$ compromised an Okta end‑user system. The attackers could reset user passwords and MFA tokens but had no ability to create or delete accounts or download customer data.
Impact
The incident exposed Okta customers to potential credential manipulation. No evidence indicates that Okta’s core services were accessed or that customer data was exfiltrated.
What to Do
- Review audit logs for unexpected password reset or MFA token changes.
- Verify that all user accounts remain valid and have not been altered.
- Enforce MFA and consider additional verification for password changes.
- Ensure your Okta deployment is running the latest version and that all security patches are applied.
- Notify affected users of the incident and advise them to monitor account activity.
Related articles
Unified Security for Multi‑Campus Universities: From Siloed to Shared Defense
Higher‑education systems confront a surge in attacks and overlapping compliance mandates, yet campus‑level security remains fragmented. Treating security as a shared capability—leveraging federated architecture and a central platform—gives end‑to‑end visibility, coordinated response, and efficient compliance.
Read briefing
Florida DMV Driver Database Breach: Stolen Police Credentials Reveal Over 200k Records
The Florida Department of Highway Safety and Motor Vehicles confirmed a breach of its DAVID driver database after the ShinyHunters extortion gang claimed to have accessed the system using stolen police credentials. The attackers exploited a compromised account belonging to a Plant City Police Department employee, who stored the login on a personal device. While ShinyHunters alleged a password‑reset flaw and claimed more than 200,000 records were exfiltrated, FLHSMV has not confirmed the exact number of records accessed. The agency has notified state authorities, halted further intrusion, and i
Read briefing
CVE-2026-70168: Windows Ancillary Function Driver for WinSock Local Privilege Escalation
A use‑after‑free flaw in the Windows Ancillary Function Driver for WinSock (CVE‑2026‑70168) lets a local user with sufficient privileges gain SYSTEM rights. The issue is limited to systems where the driver is loaded and can be mitigated by applying the latest Windows update or disabling the driver if not needed.
Read briefing
Apple Tightens macOS Full Disk Access Controls Amid AI Agent Privacy Risks
Apple announced updates to macOS Full Disk Access (FDA) to curb privacy risks posed by AI agents that can read user data. The change follows incidents where AI tools like Meta’s Muse accessed private iMessages after users granted FDA. Defenders should review which apps have FDA, disable unnecessary access, and monitor for AI agents.
Read briefing