
Threat Intel
Salient Botnet Disruption: CrowdStrike & Partners Neutralize Sality P2P Network
CrowdStrike, together with law‑enforcement and industry partners, carried out a coordinated operation that dismantled the Sality peer‑to‑peer botnet. The disruption severed the command‑and‑control infrastructure and isolated infected hosts. Defenders should validate detection rules, patch vulnerable systems, and monitor for residual activity.
What Happened
CrowdStrike collaborated with international law‑enforcement agencies and industry partners to execute a coordinated disruption of the Sality peer‑to‑peer botnet. The operation targeted the botnet’s command‑and‑control nodes, effectively severing the network’s ability to issue commands to compromised machines.
Impact
The Sality botnet, known for spreading through malicious downloads and exploiting Windows vulnerabilities, was rendered inoperable. Infected hosts were isolated, and the botnet’s ability to distribute malware and exfiltrate data was halted. The disruption also prevented further use of the botnet for credential theft and ransomware distribution.
Defensive Actions
- Verify that your detection rules for Sality signatures are enabled and up to date.
- Apply the latest Windows security patches, especially those addressing the vulnerabilities exploited by Sality.
- Conduct a network scan for residual botnet components and isolate any compromised endpoints.
- Update endpoint protection platforms with the latest threat intelligence feeds covering Sality.
- Review and tighten outbound traffic controls to block known Sality command‑and‑control domains.
Next Steps
Maintain continuous monitoring for any re‑emergence of Sality activity. Share findings with threat‑intel communities to aid in broader disruption efforts. Keep incident response playbooks updated to reflect the latest disruption tactics.
Related articles
CrowdStrike & Partners Strike Down Sality Botnet in Coordinated Disruption
In a joint effort with international law‑enforcement agencies and industry allies, CrowdStrike executed the “Peer Pressure” operation to dismantle the Sality peer‑to‑peer botnet. The campaign severed command‑and‑control channels, seized malicious infrastructure, and disrupted the botnet’s ability to distribute ransomware and other payloads. The takedown removes a key threat vector that has infected millions of hosts worldwide, demonstrating the power of coordinated cyber‑defense operations.
Read briefing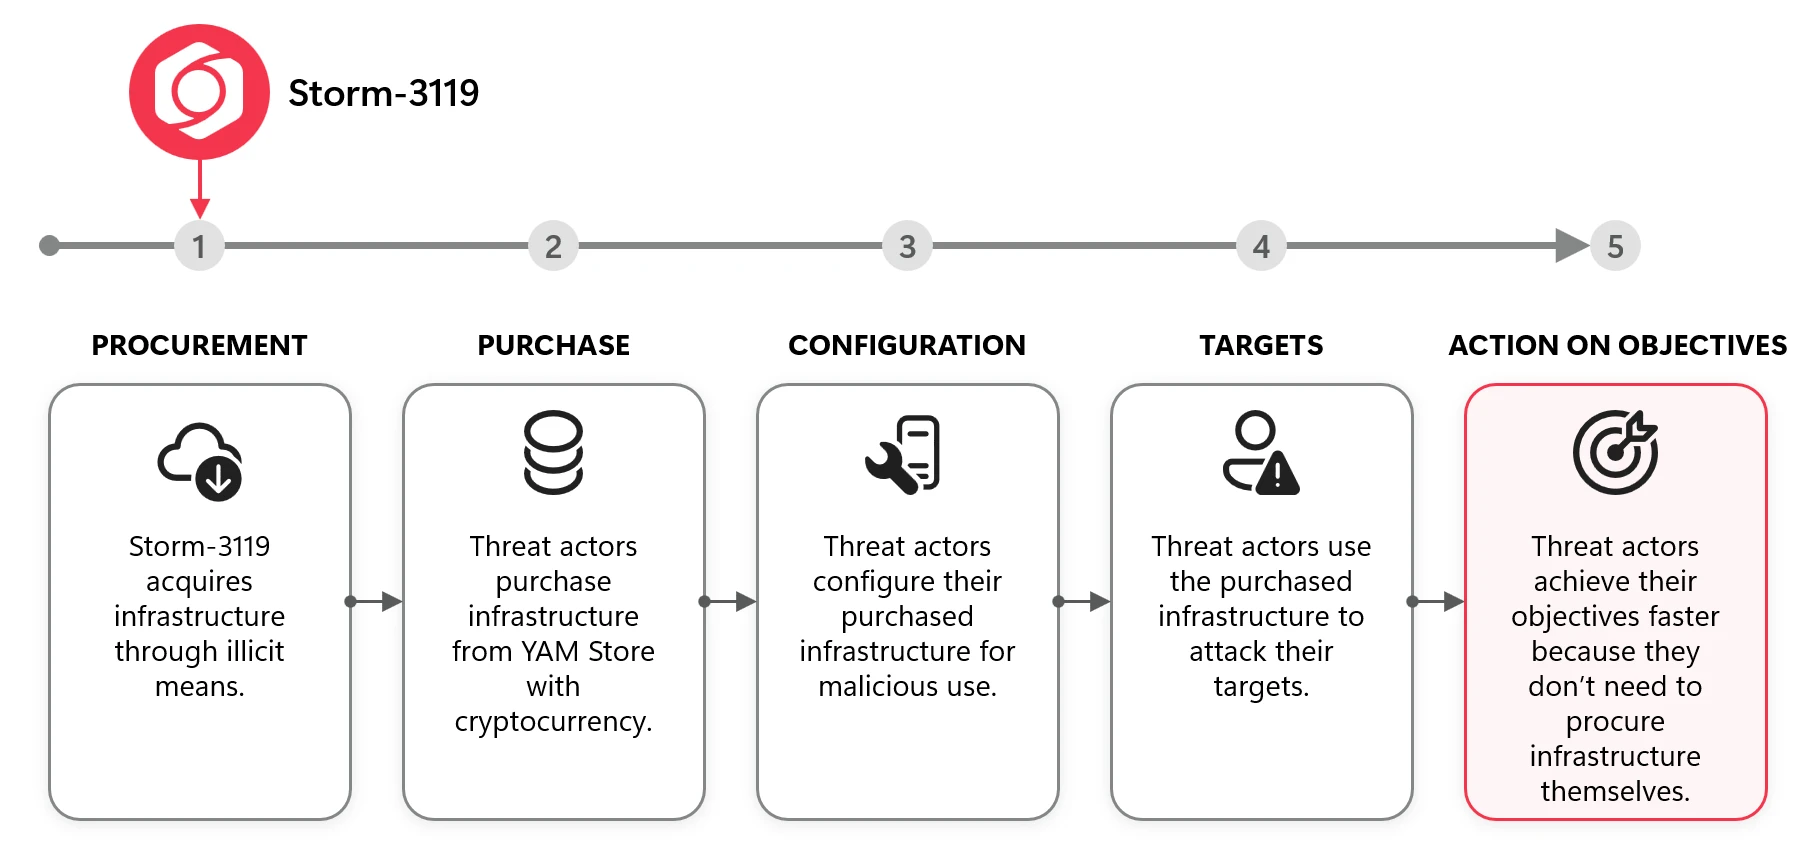
Disruption of Chinese Phishing Kit Ecosystem: Storm-2990 & YAM Store
Microsoft’s Digital Crimes Unit exposed a Chinese‑language phishing kit ecosystem, including the Storm‑2990 developers and the YAM Store marketplace (Storm‑3119). The network distributed over 1 billion phishing emails and SMS to more than 75 000 organizations in healthcare, finance, wholesale, and IT sectors across Japan, the U.S., Australia, and India. Defenders should block known phishing kit domains, monitor for compromised cloud credentials, and apply Microsoft Defender detections.
Read briefing
Google Disrupts NetNut Residential Proxy Network, Cuts Millions of Devices
Google, in partnership with the FBI and Lumen, disabled accounts and services tied to NetNut’s Popa proxy network, shared SDK and C2 intelligence, and triggered Play Protect warnings. The action has removed millions of devices from the botnet and is expected to ripple across the residential proxy ecosystem.
Read briefing
AI-Driven ARTEX Campaign Targets South Korean Financial Institutions
A covert threat actor deployed the AI‑powered ARTEX tool to infiltrate South Korean banks, exfiltrating sensitive data. CrowdStrike intelligence mapped the infrastructure and identified the attack vectors. Defenders should harden endpoint detection, monitor for ARTEX signatures, and enforce strict network segmentation.
Read briefing