
Threat Intel
Silent Phases of Intrusion: How Attackers Exploit Alert Gaps and What SOCs Must Do
Attackers now spend days or weeks in an environment generating only routine traffic, evading traditional alerting. When a high‑severity alert finally appears, the compromise is often well advanced. This briefing explains how to use network telemetry and AI‑assisted correlation to uncover the silent progression and protect your organization.
What happened
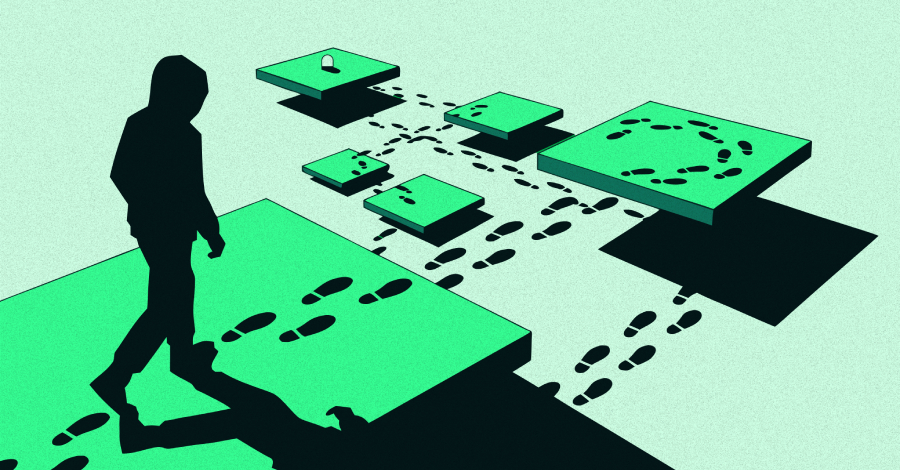
In recent weeks, SOC teams across multiple industries have reported a pattern of low‑volume, high‑impact intrusions that only surface after a prolonged, low‑alert activity phase. Attackers initiate the compromise with legitimate credentials or stolen accounts, then conduct reconnaissance and lateral movement while generating only routine network events that blend into normal traffic. The first high‑severity alert—often a malware hash match or a sudden spike in failed logins—usually appears only after the adversary has already established persistence and moved laterally.
Because the early stages of the attack produce minimal or no alerts, the incident response process is triggered too late. By the time analysts see the first red flag, the adversary may have already exfiltrated data or deployed ransomware, making containment and recovery far more difficult.
Who is affected
Any organization that relies on traditional SIEM alerting without contextual network telemetry is at risk. Mid‑market enterprises, managed service providers, and even large enterprises that have not integrated NDR or AI‑assisted correlation tools often find themselves overwhelmed by alert noise while missing the silent progression of an intrusion.
Defenders who have not adopted network‑level visibility—such as flow logs, DNS query logs, or SMB traffic analysis—are particularly vulnerable because these data sources are the ones that allow the stitching together of disparate alerts into a coherent timeline.
Impact
When attackers exploit the quiet intervals between alerts, the damage can be extensive. Persistence mechanisms such as scheduled tasks, compromised service accounts, or malicious PowerShell scripts can remain dormant for weeks, allowing the threat actor to move laterally, establish footholds, and exfiltrate data at a rate that is difficult to detect.
In many cases, the first visible alert is a high‑severity event that signals a breach already in progress. By then, the attacker may have already accessed privileged accounts, compromised critical infrastructure, or installed backdoors that survive even after the initial alert is addressed.
Exposure
Attackers deliberately use legitimate tools—such as LDAP queries, DNS lookups, or SMB file shares—to conduct reconnaissance. These actions generate normal traffic patterns that are often filtered out by security teams that focus on signature‑based alerts. The result is a blind spot where the adversary can map the network, identify vulnerable hosts, and plan lateral movement.
Because many SOCs treat each alert as an isolated incident, the chain of events that leads to a compromise is rarely reconstructed. This fragmented view prevents defenders from understanding the full scope of the intrusion, leading to incomplete containment and remediation.
What to do
- Integrate NDR or flow‑based telemetry into your SIEM to correlate low‑volume events with high‑severity alerts.
- Enable AI‑assisted timeline reconstruction to automatically stitch together related alerts and network flows.
- Implement continuous monitoring of routine protocols (LDAP, DNS, SMB) and set thresholds that trigger investigation when patterns deviate from baseline.
- Adopt a “least‑privilege” model and enforce multi‑factor authentication to reduce the risk of credential compromise.
- Conduct regular red‑team exercises that simulate silent reconnaissance to validate detection coverage.
What to watch
- Unusual spikes in LDAP or DNS traffic that correlate with known malicious domains.
- Repeated failed login attempts followed by a sudden surge in successful authentications.
- Unexpected SMB file transfers to or from privileged accounts.
- New scheduled tasks or PowerShell scripts that appear without a clear business justification.
- Persistent connections to external IPs that are not part of normal business operations.
Conclusion
Defenders must shift from a reactive, alert‑centric posture to a proactive, context‑driven strategy. By leveraging network telemetry and AI‑driven correlation, SOC teams can uncover the silent phases of an intrusion before the high‑severity alert triggers. This approach not only improves detection accuracy but also shortens the window of opportunity for attackers, reducing the overall impact of a breach.
'Detection is only as good as the context you can provide.' – Security Lead
Related vulnerabilities
CrowdStrike Updates Prompt Injection Taxonomy to Cover Autonomous Agent Planning Attacks
CrowdStrike has released an updated Prompt Injection Taxonomy that specifically addresses attack vectors targeting the planning and reasoning phases of autonomous AI agents. This update highlights how adversaries can manipulate agent decision-making processes to bypass traditional guardrails. Defenders must immediately audit agent architectures for indirect injection vulnerabilities and implement strict output validation.
Read briefing
Addressing Continuous Authorization Challenges in Zero Trust Deployments
Organizations are struggling to enforce continuous authorization within Zero Trust frameworks, creating gaps that attackers exploit. Defenders in critical infrastructure and enterprise environments must adopt context‑aware, AI‑driven authorization and integrate with unified platforms like CrowdStrike Falcon to close these gaps.
Read briefing
Inside the First Hours of a Google Workspace Breach: Live Webinar Reveals What Works and What Doesn’t
BleepingComputer partners with Material Security to host a live deep‑dive on how fast‑growing firms handle Google Workspace intrusions. The session dissects real breaches where attackers used social engineering and rogue OAuth apps, highlighting the critical early decisions that can either curb damage or amplify it. Attendees learn which controls deliver the most bang for lean security teams and hear the speakers’ take on building a resilient Workspace strategy from scratch.
Read briefing
Microsoft Office Excel for Mac Remote Code Execution Vulnerability CVE-2026-97010 – Update Required
A remote code execution flaw in Microsoft Office Excel for Mac (CVE‑2026‑97010) allows attackers to run arbitrary code via a crafted workbook. Only the Mac version of Excel is affected; other Office products do not require action. Defenders must install the latest Mac update immediately.
Read briefing