
Threat Intel
SMS Pumping: Fraudsters Exploit Verification to Drain Business Revenue
SMS pumping is a fraud technique that tricks verification systems into sending bulk messages, inflating traffic and generating illicit revenue for attackers. The attack targets businesses using SMS‑based authentication, draining resources and exposing sensitive data. Defenders should enforce rate limits, validate message sources, and adopt multi‑factor authentication to mitigate the threat.
SMS pumping is a deceptive scheme where attackers trigger automated SMS verification requests to inflate traffic and siphon revenue from businesses.
What Happened
Fraudsters exploit the trust placed in SMS‑based two‑factor authentication by sending repeated verification codes to the same number or a pool of numbers, causing service providers to bill the victim for each message.
Impact
Businesses experience unexpected spikes in SMS costs, potential account lockouts, and exposure of sensitive user data. The technique can also overwhelm messaging APIs, leading to denial‑of‑service conditions.
Mitigation Steps
- Implement per‑user and per‑IP rate limits on verification requests.
- Validate the originating phone number against a whitelist of trusted carriers.
- Use alternative second factors (app‑based authenticators, push notifications).
- Monitor SMS usage patterns for sudden surges and trigger alerts.
- Apply message throttling and CAPTCHAs for suspicious traffic.
Early detection and strict rate‑limiting are the most effective defenses against SMS pumping.
Related vulnerabilities
Geopolitical Turmoil Fuels Targeted Scams: What SecOps Need to Know
Conflict zones provide fertile ground for fraudsters who use current events to craft convincing phishing, romance, and charity scams. Defenders should enforce MFA, scrutinize unsolicited requests, and educate users on verification steps. Monitoring for suspicious communications and blocking known malicious domains can reduce impact.
Read briefing
Zero Trust Onboarding Gap Exposes New Users to Attackers
Zero Trust models assume continuous verification, yet the initial onboarding step remains a weak point. Attackers can exploit the day‑one window before MFA or strong authentication is in place. Defenders must enforce pre‑onboarding identity verification and automate workflows to close this gap.
Read briefing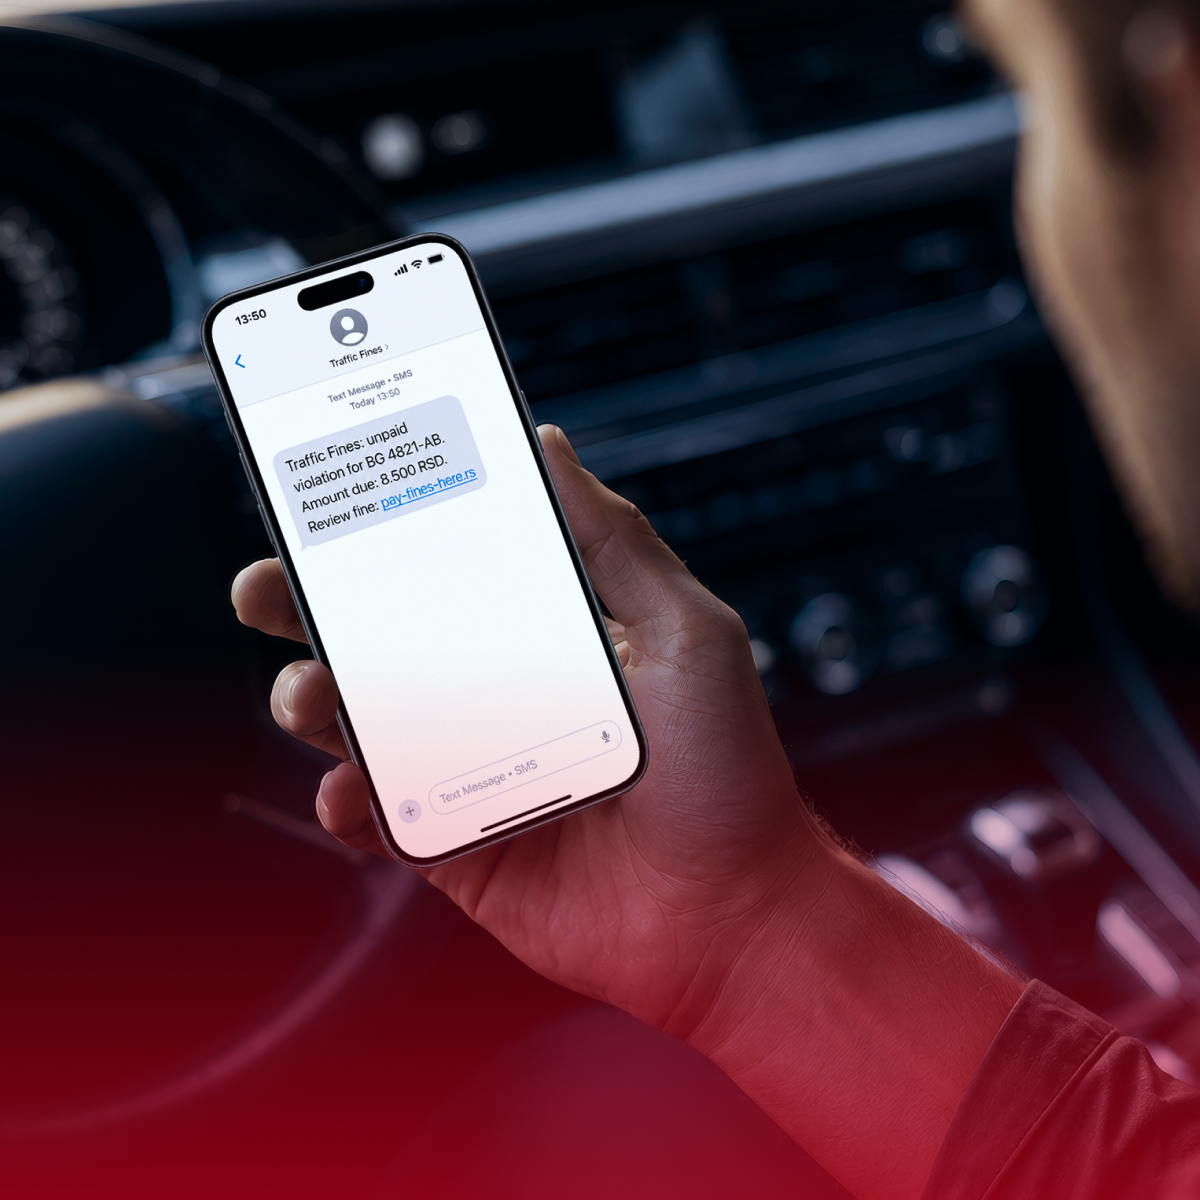
SMS Phishing Targeting Serbian Road Users via Fake State Authority – Global Threat
An SMS phishing operation impersonating Serbia’s state road authority has been linked to the Darcula and Phoenix PhaaS platforms, affecting motorists in Serbia and other countries. The campaign uses spoofed numbers and fake traffic fines to lure victims into revealing credentials. Defenders should verify SMS authenticity, block spoofed numbers, and monitor for related phishing indicators.
Read briefing
LinkedIn Introduces Verification Checks to Counter AI‑Generated Fake Profiles
LinkedIn has rolled out new verification mechanisms—peer‑vouching, company‑page controls, and workplace email validation—to make fabricated professional identities harder to create. Defenders should cross‑reference hires against LinkedIn’s verified data and enforce workplace email verification before granting internal access.
Read briefing