
Threat Intel
WeaselBiscuit JavaScript Stealer Discovered Across 13 Malicious npm Packages
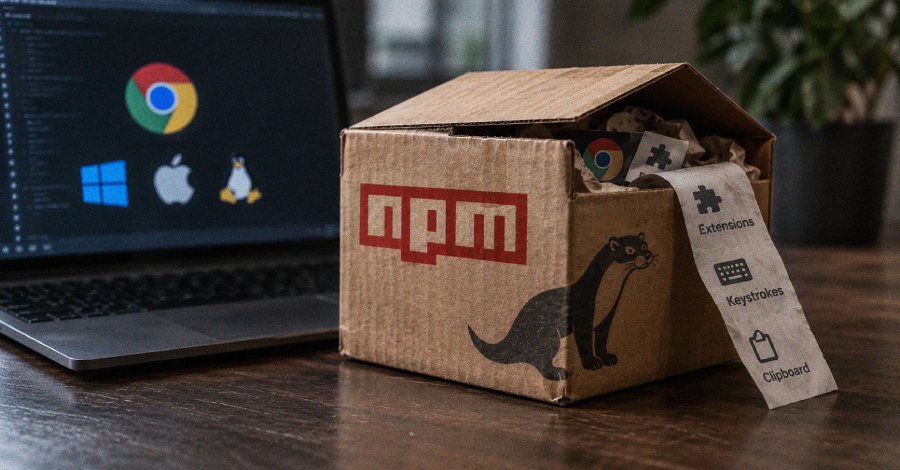
Security researchers have identified 13 malicious npm packages distributing a lightweight JavaScript information stealer designated WeaselBiscuit. Linked functionally to DPRK-associated campaigns, the malware specifically targets browser extension storage on infected developer workstations.
What Happened
A cluster of 13 malicious npm packages has been identified deploying a previously undocumented JavaScript information stealer dubbed WeaselBiscuit. Security researchers note that while WeaselBiscuit is significantly smaller and more streamlined than typical credential stealers, it shares functional overlaps with the BeaverTail and OtterCookie malware families linked to North Korean threat actor campaigns targeting software developers.
The malicious payload is triggered automatically when a developer imports any of the compromised packages into a project. A bundled loader script ("loader.js") then fetches the core stealer from an external dead drop hosted on Npoint and executes the code directly in memory.
Impact and Capabilities
WeaselBiscuit focuses primarily on local data extraction without deploying heavy remote access trojans (RATs) or persistence mechanisms. Its core functionality centers on harvesting sensitive data stored within Chromium-based browser extensions.
- Compromised packages include:
@biz44/id10-client,@biz44/id12-client,@biz44/id44-client,@biz44/id79-client,@biz44/id95-client,@biz44/id99-client,@biz44/process-runtime-utils,@biz44/runtime-utils,engin1,id79-client,process-lhpm,process-mite, andprocess-tailwind. - Cross-platform threat affecting Windows, macOS, and Linux developer environments.
- Extracts browser extension storage, potentially compromising authentication tokens, crypto wallet data, and session materials.
What to Do
SecOps teams and system administrators managing developer endpoints should immediately audit internal package dependencies for any references to the identified malicious npm packages.
- Block or remove the affected 13 npm packages from all repositories and local developer projects.
- Revoke active session tokens and credentials for developer workstations that ingested the malicious modules.
- Implement software composition analysis (SCA) tooling to detect typosquatting and unauthorized third-party dependencies in build pipelines.
Related articles
Sophisticated Malicious npm Packages Utilize Advanced Defense Evasion Techniques
Analysts have identified a highly sophisticated set of malicious npm packages featuring advanced defense evasion tactics. While technical indicators suggest state-level capabilities, concrete attribution remains unconfirmed. SecOps teams and JavaScript developers must review supply chain dependencies immediately.
Read briefing
WaterPlum Infected 30,000 Devices via Job‑Seeking Phishing, Stole $10.7M in Crypto
From December 2025 to July 2026, the North Korean group WaterPlum compromised over 30,000 devices worldwide, siphoning more than $10.7 million in cryptocurrency. The campaign, part of the “Contagious Interview” effort, lured job seekers with malicious npm packages and fake interview prompts. Defenders should vet third‑party code, monitor npm traffic, and enforce application whitelisting.
Read briefing
PhantomRaven: LLM‑Generated JavaScript Stealer Used by Bug‑Bounty Threat Actor
CrowdStrike uncovered PhantomRaven, a JavaScript‑based information stealer crafted with large‑language‑model techniques and distributed by a financially motivated threat actor who masquerades as a bug‑bounty hunter. The tool harvests credentials and personal data from compromised web pages. Defenders should block known malicious domains, harden client‑side scripting controls, and monitor for suspicious JavaScript payloads.
Read briefing
GitHub Enforces 48‑Hour Expiry on npm Trusted Publishing to Curb Package Hijacking
GitHub has added a 48‑hour expiration window for unvalidated npm trusted publishing configurations, a response to a flaw that allowed attackers to publish malicious versions of other users’ packages without credential theft. The change affects over 1,500 npm packages that were previously vulnerable and requires developers to validate their trusted publisher bindings within two days. Defenders should review existing configurations, ensure timely validation, and tighten CI/CD token handling.
Read briefing