
Threat Intel
Defending Against China‑Nexus Covert Networks of Compromised Edge Devices
China‑aligned actors are building large covert networks of compromised routers and edge devices to conduct reconnaissance, malware delivery, and command‑and‑control. Organisations must map and baseline edge‑device traffic, focus on VPN and remote‑access flows, and deploy dynamic threat‑feed filtering that includes known covert‑network indicators. These measures help detect and isolate compromised devices before they can be leveraged in an attack chain.
What Happened
China‑aligned cyber actors have shifted from using individually procured infrastructure to operating large covert networks built from compromised routers and other edge devices. These botnets support all stages of the Cyber Kill Chain, from reconnaissance to command and control.
Impact
Compromised edge devices can silently exfiltrate data, host malicious payloads, and serve as footholds for lateral movement. Because they often sit behind firewalls and are overlooked, they provide a low‑visibility attack surface that can be leveraged by adversaries to bypass perimeter defenses.
What to Do
- Map and baseline normal traffic for all edge devices, with a focus on VPN and remote‑access connections.
- Implement dynamic threat‑feed filtering that includes indicators of covert networks identified by NCSC.
- Regularly audit device firmware and patch known vulnerabilities on routers and IoT endpoints.
- Deploy network segmentation and micro‑segmentation to isolate edge devices from critical assets.
- Monitor for anomalous outbound traffic patterns that may signal a compromised device.
Related articles
Proxyjacking Campaign Hijacks Edge Devices to Serve Residential Proxies – 143 Devices in 34 Countries
A proxyjacking operation was uncovered by GreyNoise during a live demo, affecting 143 edge devices across 34 countries. The attackers used compromised devices to route traffic through residential IPs, masking malicious activity. Defenders should audit edge device integrity, block identified malicious IPs, and monitor Entra ID sign‑in logs for anomalous residential sources.
Read briefing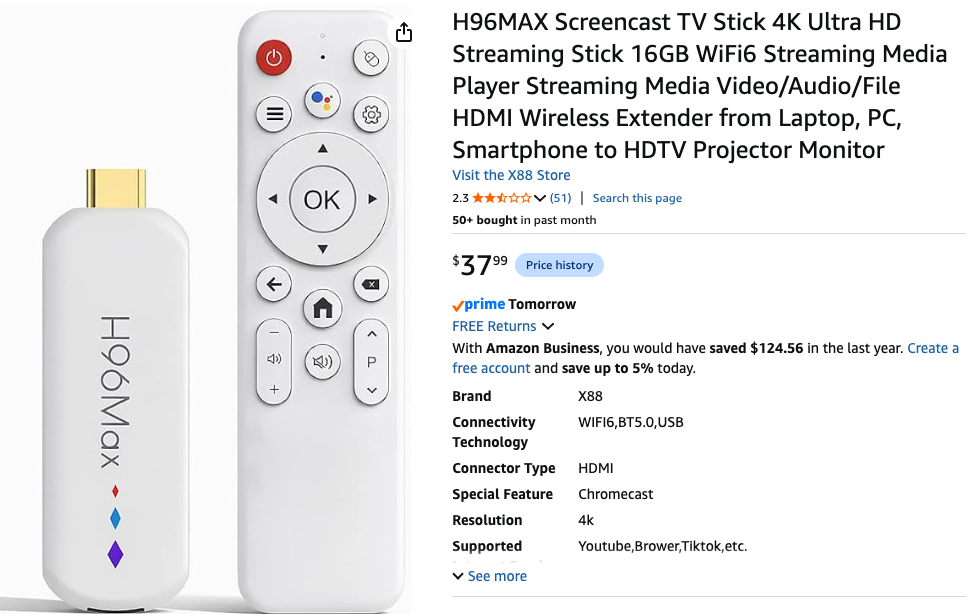
Generic H96 Android TV Sticks Weaponized for Large-Scale Ad Fraud
Security researchers have uncovered a widespread ad fraud scheme operating through popular, low-cost H96 generic TV streaming sticks. These compromised devices spoof mobile phone user-agents to execute automated, fake ad clicks on AI-generated websites via hidden backdoors tied to a mainland China firm.
Read briefing
React2Shell Exploitation Surge: Automated Scans Target Vulnerable React Server Components
Over the past 10 days the React2Shell campaign has flooded networks with automated probes against vulnerable React Server Components. Most traffic consists of 200‑500‑byte payloads, indicating scripted scanners, while a minority of 1,000‑byte payloads carry actual malicious code. Defenders should harden React deployments, monitor for these size patterns, and leverage GreyNoise blocklists.
Read briefing
AI-Orchestrated Campaign Targets PaperCut NG/MF Vulnerabilities
Threat intelligence sensors have detected an automated campaign leveraging AI to develop and launch exploits against PaperCut NG/MF print management software. The attacks successfully compromised multiple organizations across dozens of countries by targeting critical remote code execution flaws.
Read briefing