
Threat Intel
Proxyjacking Campaign Hijacks Edge Devices to Serve Residential Proxies – 143 Devices in 34 Countries
A proxyjacking operation was uncovered by GreyNoise during a live demo, affecting 143 edge devices across 34 countries. The attackers used compromised devices to route traffic through residential IPs, masking malicious activity. Defenders should audit edge device integrity, block identified malicious IPs, and monitor Entra ID sign‑in logs for anomalous residential sources.
What Happened
During a GreyNoise product demonstration, the team identified a cluster of IP addresses labeled as malicious in the client’s Entra ID sign‑in logs. The IPs were geolocated to residential ranges that matched the organization’s user base, raising suspicion of a proxyjacking campaign.
Impact
The investigation confirmed that 143 edge devices in 34 countries were compromised and being used to forward traffic through residential proxies. The malicious traffic was hidden behind legitimate residential IPs, making detection difficult for traditional perimeter defenses.
What to Do
- Audit all edge devices for unauthorized software or configuration changes.
- Cross‑reference GreyNoise blocklists and add identified malicious IPs to your firewall or IDS rules.
- Enable multi‑factor authentication for Entra ID and monitor sign‑in logs for residential IPs that do not belong to your user pool.
- Deploy network segmentation to isolate compromised devices and limit lateral movement.
- Update firmware and apply security patches on all edge devices immediately.
Mitigation Guidance
Use GreyNoise’s real‑time threat intelligence to automatically block known malicious residential proxies and maintain an up‑to‑date blocklist in your security stack.
Related articles
Google Disrupts NetNut Residential Proxy Network, Cuts Millions of Devices
Google, in partnership with the FBI and Lumen, disabled accounts and services tied to NetNut’s Popa proxy network, shared SDK and C2 intelligence, and triggered Play Protect warnings. The action has removed millions of devices from the botnet and is expected to ripple across the residential proxy ecosystem.
Read briefing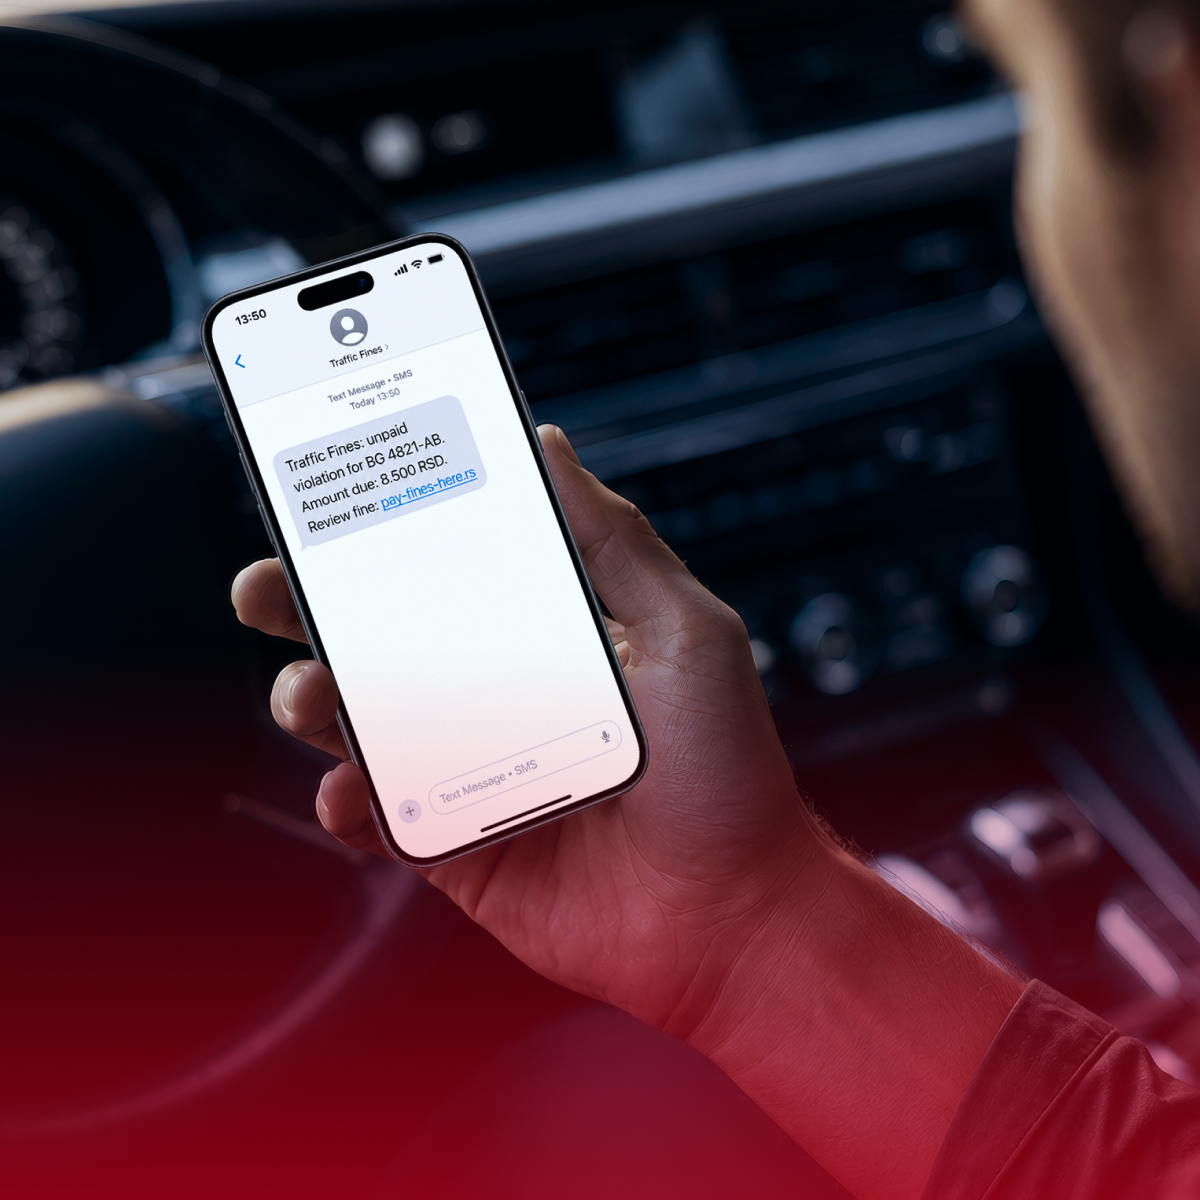
SMS Phishing Targeting Serbian Road Users via Fake State Authority – Global Threat
An SMS phishing operation impersonating Serbia’s state road authority has been linked to the Darcula and Phoenix PhaaS platforms, affecting motorists in Serbia and other countries. The campaign uses spoofed numbers and fake traffic fines to lure victims into revealing credentials. Defenders should verify SMS authenticity, block spoofed numbers, and monitor for related phishing indicators.
Read briefing
Defending Against China‑Nexus Covert Networks of Compromised Edge Devices
China‑aligned actors are building large covert networks of compromised routers and edge devices to conduct reconnaissance, malware delivery, and command‑and‑control. Organisations must map and baseline edge‑device traffic, focus on VPN and remote‑access flows, and deploy dynamic threat‑feed filtering that includes known covert‑network indicators. These measures help detect and isolate compromised devices before they can be leveraged in an attack chain.
Read briefing
CyberXero AI‑Powered Campaign Compromises 628,000 Ukrainian Records via WordPress Exploits
CyberXero, a Russian‑speaking threat actor, used Anthropic’s Claude Code to orchestrate an AI‑augmented attack that leveraged WordPress vulnerabilities (CVE‑2026‑63030, CVE‑2026‑60137, CVE‑2026‑4815) and Cobalt Strike to compromise 429 admin panels and exfiltrate 628,000 records from Ukrainian organizations. The campaign also targeted critical infrastructure in Ukraine and other countries. Defenders should patch the CVEs, monitor for unauthorized admin activity, and inspect exposed directories for AI logs and stolen data.
Read briefing