
Malware
Deimos Remote Access Tool: Updated TTPs and Elastic Security C2 Takedown
Elastic Security dismantled the command‑and‑control infrastructure of the Deimos remote‑access implant, exposing its advanced obfuscation and signed lure tactics. The implant delivers initial access, persistence, and full C2 capabilities, making it a potent threat. Defenders should block known C2 endpoints, deploy detection rules, and monitor for suspicious signed binaries.
What happened
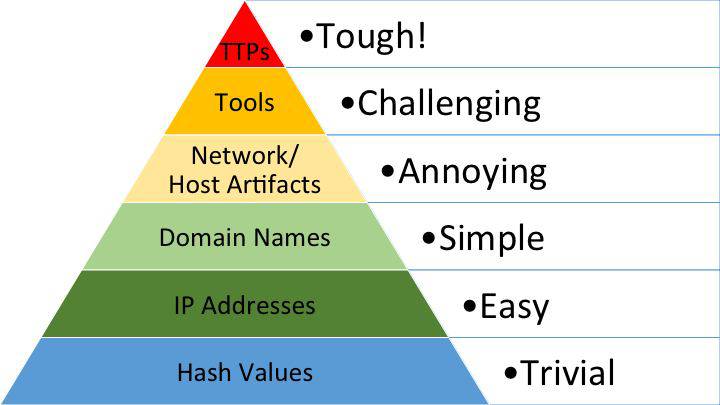
The Elastic Security team discovered a new strain of the Deimos remote‑access implant, first seen in 2020, that has been actively refined with advanced obfuscation, encryption, and digitally signed lure files. A recent takedown of the implant’s command‑and‑control infrastructure was completed, exposing the C2 domains and IPs used by the malware.
Impact
Deimos provides attackers with initial foothold, persistence, and full C2 capabilities. The use of convincing signed executables and multi‑layer obfuscation makes detection difficult, allowing the implant to remain hidden in compromised environments and potentially be sold to other threat actors.
What to do
- Block the known C2 domains and IP addresses listed in the takedown report.
- Deploy Elastic Security detection rules that flag execution of signed binaries with suspicious file paths or hash patterns matching Deimos samples.
- Monitor for outbound traffic to the identified C2 endpoints and for processes that spawn remote shells or download additional payloads.
- Verify the integrity of signed installers by checking publisher certificates against known malicious issuers.
- Apply the provided hunting queries to search for the implant’s unique indicators of compromise in your logs.
Mitigation
Implement least‑privilege access controls, enforce application whitelisting, and enable file integrity monitoring to detect unauthorized signed binaries. Keep the Elastic Stack updated with the latest detection rules and threat intelligence feeds.
Related articles
Elastic Security Labs Releases NETWIRE Configuration Extractor to Aid Detection
Elastic Security Labs has released a free tool that dynamically extracts encrypted configuration data from the NETWIRE RAT, a malware variant that has risen in prevalence since 2022. The extractor uses YARA and Capstone to locate RC4 keys and decrypt payloads, enabling defenders to expose C2 endpoints and credentials quickly.
Read briefing
Elastic Security Releases BPFDoor Configuration Extractor Tool
Elastic Security has published a Python‑based extractor that pulls hard‑coded passwords from BPFDoor samples. The tool can be run in Docker or locally via Poetry and supports single files or directories. Defenders should run it against suspected BPFDoor binaries to recover credentials and improve incident response.
Read briefing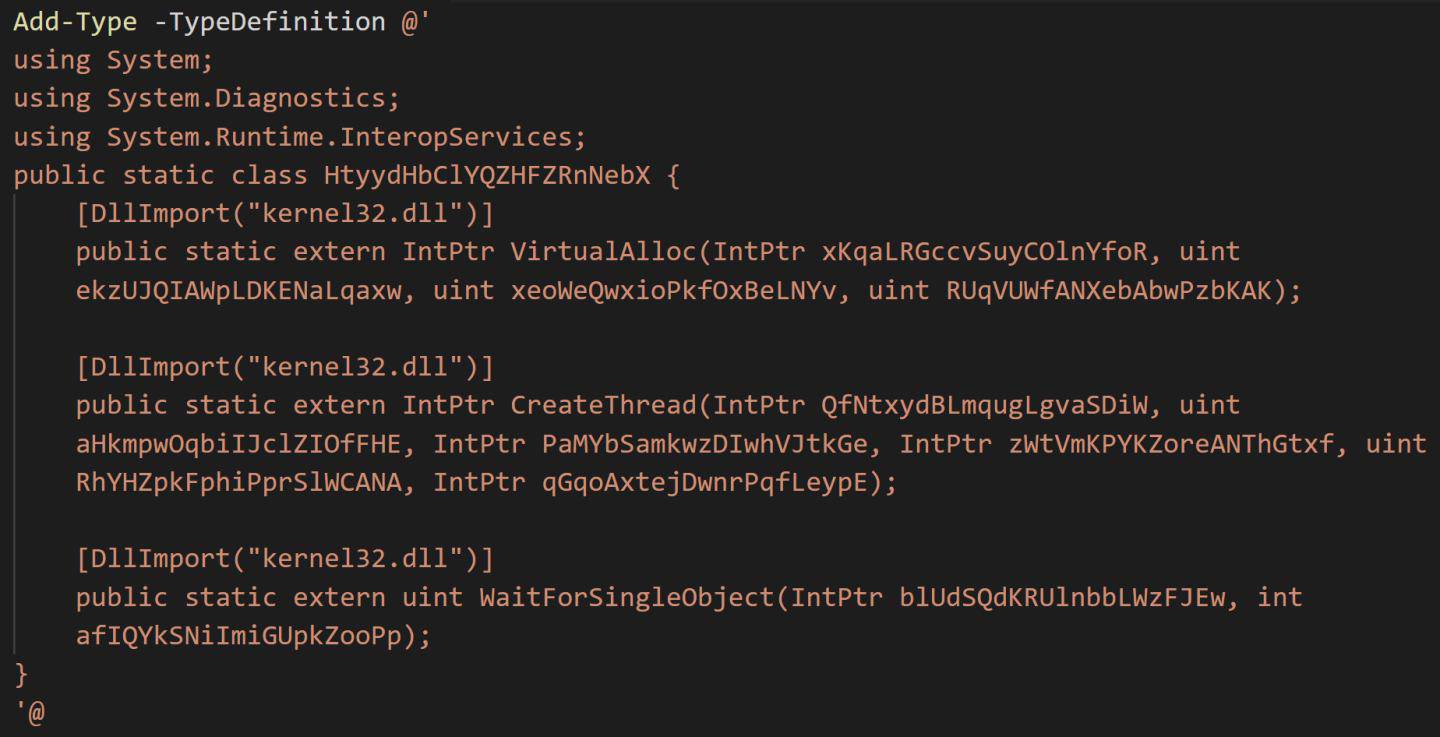
BUGHATCH Malware: In-Memory PowerShell Implant from CUBA Campaign
BUGHATCH is a custom C2 implant discovered in February 2022 during the CUBA ransomware operation. The tool is delivered via an obfuscated PowerShell dropper, loads in memory, and can download and execute arbitrary code using reflection, shellcode, or system commands. Defenders should block the dropper, monitor for suspicious download activity, and deploy the provided YARA rule.
Read briefing
GoldPickaxe iOS Trojan: Face‑ID Stealer and How to Detect It
GoldPickaxe is a new iOS Trojan that harvests Face‑ID data and exfiltrates it to remote servers. The malware targets iOS 14+ devices, exploiting a flaw in the biometric framework. Defenders should enforce strict app vetting, monitor for unauthorized biometric usage, and keep devices updated.
Read briefing