
Threat Intel
Detecting Hotkey‑Based Keyloggers via Undocumented Kernel Hotkey Table
Elastic Security Labs uncovered a new Windows keylogger technique that hijacks the RegisterHotKey API to capture keystrokes. The detection method uses the undocumented kernel hotkey table and ETW events from the Win32k provider, and is available in Elastic Defend 8.12.
What happened
Elastic Security Labs identified a new class of Windows keyloggers that hijack the operating system’s hotkey registration API to silently capture keystrokes. The technique was first demonstrated in a proof‑of‑concept called Hotkeyz, released by Microsoft researcher Jonathan Bar Or, and relies on the undocumented hotkey table in kernel space.
Impact
These hotkey‑based keyloggers can run with the same privileges as the user that registered the hotkey, allowing attackers to record sensitive input without triggering typical hook or polling detections. The attack is compatible with Windows 10 22H2 (build 19045.5371) and can evade many endpoint‑detection solutions that focus on user‑mode APIs.
Detection technique
Elastic introduced a behavior‑based rule in Elastic Defend 8.12 that listens to the Microsoft‑Windows‑Win32k ETW provider. By correlating RegisterHotKey events with subsequent WM_HOTKEY messages that are not matched to legitimate applications, the rule flags suspicious hotkey registrations. The rule also checks the undocumented kernel hotkey table for entries that persist after the registering process exits.
What to do
- Upgrade to Elastic Defend 8.12 or later and enable the hotkey‑keylogger rule.
- Configure ETW collection for the Win32k provider on all Windows endpoints and forward logs to Elastic Security.
- Review hotkey registrations in the registry and via
GetRegisteredHotKeysAPIs; revoke any that are unnecessary. - Apply the latest Windows security patches and consider disabling the RegisterHotKey API for non‑trusted applications via group policy.
- Complement the rule with user‑mode hook detection and polling‑based keylogger checks for a layered defense.
Related articles
Mirage Kitten APT Deploys NodeRabbit and PollCat RATs via Trojanized Coding Challenges
Kaspersky researchers have uncovered new campaigns by the Mirage Kitten threat group targeting aviation and FinTech sectors in the Middle East and Africa. The attacks utilize two previously undocumented cross-platform remote access trojans, NodeRabbit and PollCat, delivered via malicious job application coding challenges.
Read briefing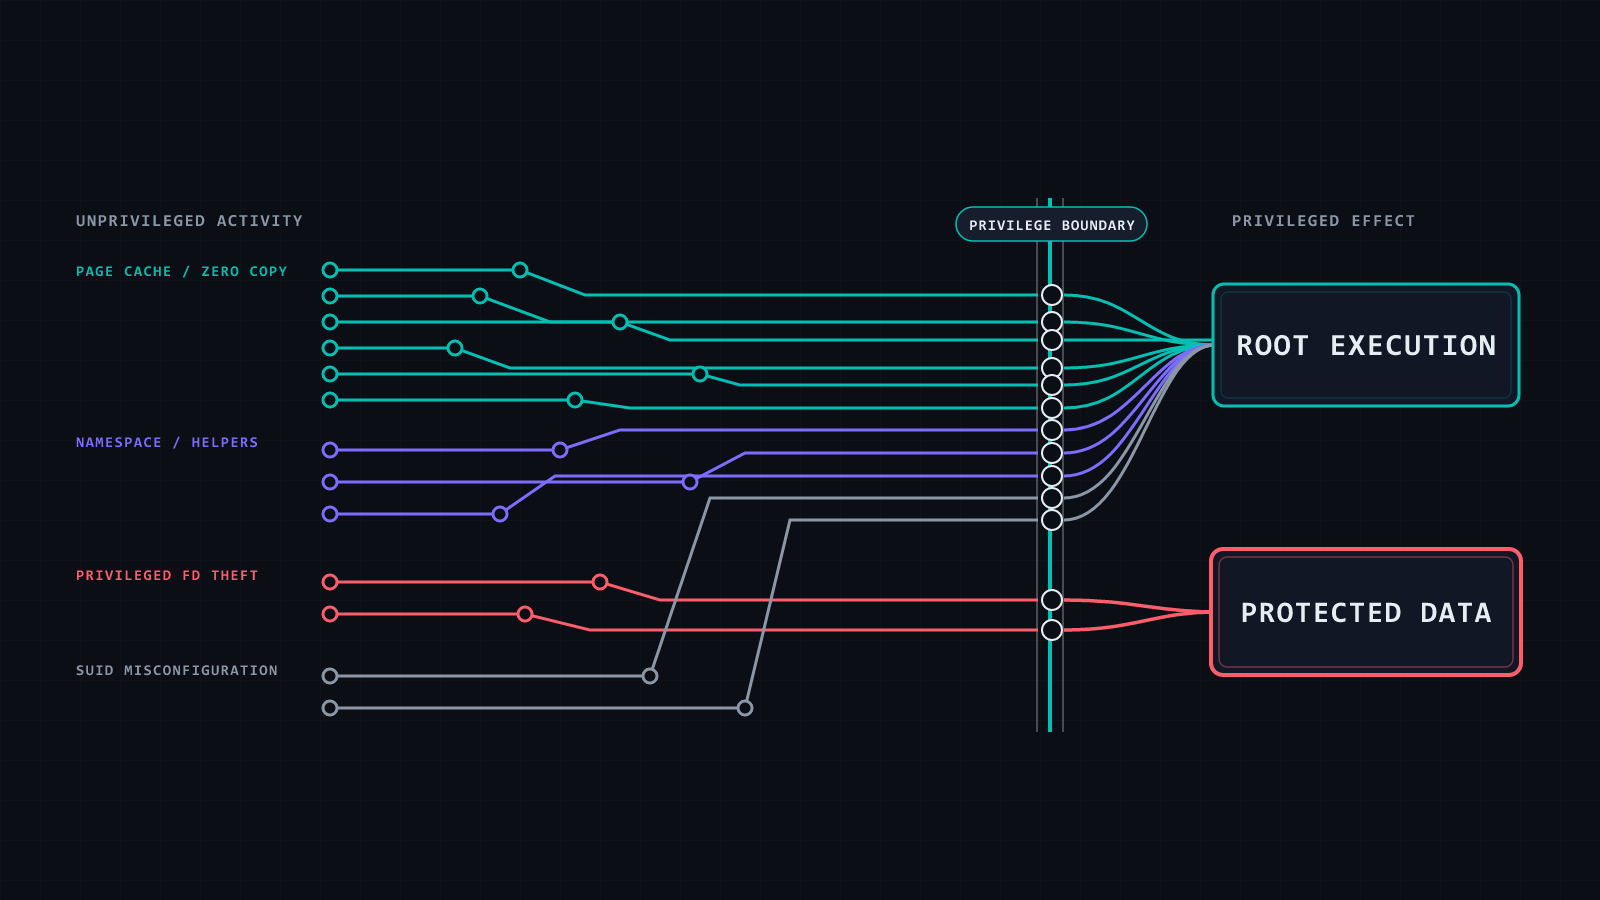
Copy‑On‑Write Chaos: Detecting the 2026 Linux Privilege Escalation Surge
In 2026 a wave of Linux privilege‑escalation CVEs exploded from a single copy‑on‑write bug, hitting kernel interfaces from networking to filesystems. RootPwn’s briefing explains how the same exploit pattern surfaces across diverse subsystems, how Elastic Defend and Auditd can surface the common escalation flow, and what rules to deploy to catch both the generic root‑gain pattern and the specific COW‑related techniques.
Read briefing
Detecting Cobalt Strike Beacons with Elastic Stack: Memory‑Based Collection and Analysis
Cobalt Strike, a popular red‑team tool, can be abused by threat actors to maintain persistence via malleable C2 beacons. Using Elastic Stack’s Fleet policy, defenders can capture shellcode and memory regions from Windows endpoints, parse beacon configurations, and surface adversary activity. The following briefing explains how to set up detection‑only policies, collect 4 MB memory samples, and analyze beacon metadata.
Read briefing
North Korean APT Breaches South Korean Media and Auto Firms via New Linux Toolkit on HAProxy Load Balancers
A suspected North Korean APT deployed a previously undocumented Linux espionage toolkit, dubbed "TED," to compromise HAProxy load balancers in South Korean media and automotive companies. The attackers leveraged the compromised appliances to harvest credentials, redirect traffic, and execute drive‑by downloads, fitting the DPRK pattern of long‑term espionage via trusted software. Rapid7 links the activity to APT37 with medium confidence, highlighting the dual focus on information control and manufacturing IP.
Read briefing