
Cybersecurity
Elastic Defend Enhances Endpoint Detection with Kernel Call Stack Enrichment
Elastic Defend has added kernel‑level call stack enrichment to its rule set, giving defenders richer context for alerts. The feature improves false‑positive and false‑negative rates and makes alert explanations clearer. Enabling it can help SecOps teams quickly pinpoint the origin of suspicious activity.
What Happened
Elastic Inc. released a new enrichment for Elastic Defend that captures kernel‑level call stacks for every event that matches its 550+ detection rules.
Impact
Defenders using Elastic Defend now receive an expanded context field in alerts, showing the sequence of user‑mode and kernel‑mode functions that led to the event. This reduces false positives by clarifying legitimate activity and surfaces hidden malicious behavior that previously slipped through.
How Call Stacks Help
- Provides a reverse‑chronological list of function calls, allowing analysts to trace the exact API chain.
- Highlights user‑initiated actions (e.g., GUI vs. command line) through user‑mode modules.
- Shows kernel drivers involved, helping to identify privilege‑escalation or file‑system tampering.
What to Do
- Enable the “kernel call stack enrichment” option in the Elastic Defend rule configuration.
- Review the new “call_stack” field in alert payloads and adjust rule thresholds if you notice an increase in noise.
- Use the stack trace to correlate with other telemetry (process creation, file writes) for deeper investigation.
- Document common benign patterns to refine false‑positive filters.
Next Steps
Regularly update Elastic Defend to the latest version to benefit from ongoing improvements to call‑stack parsing and rule accuracy.
Related articles
Detecting Hotkey‑Based Keyloggers via Undocumented Kernel Hotkey Table
Elastic Security Labs uncovered a new Windows keylogger technique that hijacks the RegisterHotKey API to capture keystrokes. The detection method uses the undocumented kernel hotkey table and ETW events from the Win32k provider, and is available in Elastic Defend 8.12.
Read briefing
Using Auditd and Auditd Manager for Real‑Time Linux Detection
Auditd provides kernel‑level event logging for Linux, enabling precise detection of suspicious activity. Elastic’s Auditd Manager simplifies rule deployment across hosts, letting defenders focus on threat hunting rather than configuration drift. This briefing outlines how to enable Auditd, craft rules, and integrate with Elastic Stack for actionable alerts.
Read briefing
Elastic Security Uses Beacon Object Files to Test Detection Coverage
Elastic Security used Beacon Object Files (BOFs) during its OnWeek event to probe gaps in detection coverage. By detonating BOFs with its internal Detonate Service and analyzing telemetry via the AI Assistant for Security, the team uncovered blind spots in in‑memory execution detection. Defenders can adopt a similar BOF‑based validation workflow to strengthen their detection pipelines.
Read briefing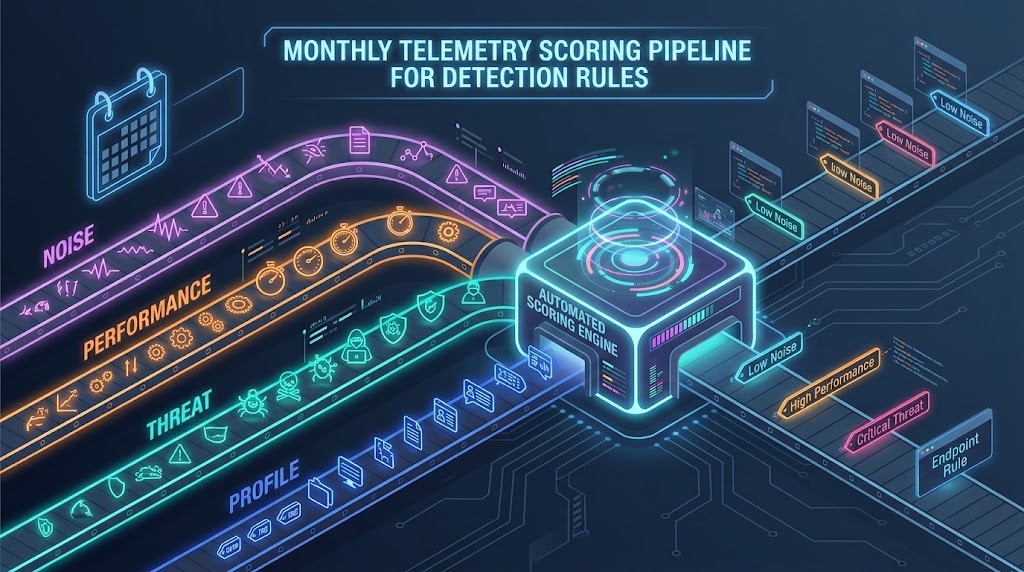
Elastic SIEM Monthly Rule Scoring: Prioritizing Detection Rules
Elastic SIEM now auto‑scores its 2,100+ prebuilt detection rules each month using real‑world telemetry, assigning Noise, Performance, Threat, and Profile tags. Security teams can use these dynamic labels to enable the most effective rules first, reduce alert fatigue, and keep detection logic aligned with evolving environments.
Read briefing