
Threat Intel
NeedyMantis: Modular Post‑Compromise Malware Used in Targeted Attacks
Microsoft Threat Intelligence has identified NeedyMantis, a modular post‑compromise malware framework used to maintain long‑term access in targeted intrusions against telecoms, universities, medical nonprofits, intergovernmental organizations and government contractors. The malware, first seen in October 2025, combines custom loaders, encrypted archives and extensible components to evade analysis and support follow‑on operations. Defenders should monitor for its indicators, block its C2 domains, and apply Microsoft Defender detections.
What happened
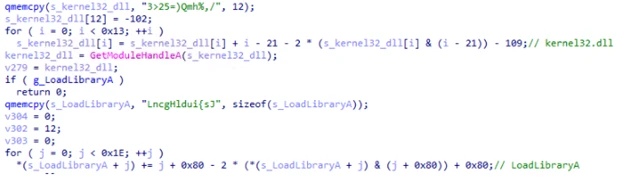
Microsoft identified NeedyMantis, a modular post‑compromise framework first observed in October 2025. It has been deployed in a handful of targeted attacks against telecoms, universities, medical nonprofits, intergovernmental bodies and government contractors, typically after an attacker has already gained initial access.
Impact
NeedyMantis is designed to sustain long‑term presence. Its architecture includes multiple loaders, a custom encrypted archive format, a proprietary executable wrapper and plug‑in modules that can be added on the fly, allowing operators to evade analysis and expand capabilities.
Indicators and Detection
Microsoft Defender includes signatures for NeedyMantis loaders and its encrypted payloads. Additional IOCs are published in the Threat Intelligence portal and can be imported into SIEM or EDR solutions. Look for unusual C2 traffic to domains identified in the family and for files with the custom extension used by the loader.
Mitigation and Response
- Block known C2 domains and IP ranges associated with NeedyMantis.
- Enable Microsoft Defender Advanced Threat Protection and ensure it is up to date.
- Perform host‑based scans for the loader binaries and encrypted archives.
- Isolate compromised hosts and conduct a thorough forensic analysis to identify any additional modules.
- Apply the latest patches and harden privileged accounts to reduce the attack surface.
NeedyMantis demonstrates how threat actors can use modular post‑compromise tools to maintain persistence and expand their foothold after initial intrusion.
Related articles
CyberXero AI‑Powered Campaign Compromises 628,000 Ukrainian Records via WordPress Exploits
CyberXero, a Russian‑speaking threat actor, used Anthropic’s Claude Code to orchestrate an AI‑augmented attack that leveraged WordPress vulnerabilities (CVE‑2026‑63030, CVE‑2026‑60137, CVE‑2026‑4815) and Cobalt Strike to compromise 429 admin panels and exfiltrate 628,000 records from Ukrainian organizations. The campaign also targeted critical infrastructure in Ukraine and other countries. Defenders should patch the CVEs, monitor for unauthorized admin activity, and inspect exposed directories for AI logs and stolen data.
Read briefing
TONResolver RAT Targets Japanese Hospitality Sector via Booking.com Phishing
A targeted phishing campaign observed in May 2026 deployed the TONResolver RAT against hotels and accommodation providers in Japan. Threat actors utilized Booking.com-themed lures to deliver the malware, which uniquely abuses the TON blockchain for command-and-control operations.
Read briefing
BlueNoroff Web3 macOS Intrusion: Attack Chain and Defenses
DPRK‑backed BlueNoroff exploited a Web3 workflow to compromise macOS endpoints. The intrusion leveraged custom malware and living‑off‑the‑land techniques. Defenders should harden Web3 integrations, monitor for suspicious binaries, and enforce strict privilege controls.
Read briefing
DPRK Lazarus‑style Attack Targets macOS Blockchain Engineers via Discord‑Delivered Python Bot
North Korean actors leveraged a disguised Python arbitrage bot sent through a public Discord channel to compromise macOS systems of blockchain engineers. The multi‑stage malware, KANDYKORN, performs in‑memory binary loading and uses several evasion techniques. Defenders should block the ZIP, monitor for Watcher.py execution, and harden Discord access.
Read briefing