
Threat Intel
SilabRAT (SnappyClient) – Darkweb‑MaaS RAT Focused on Credential Theft
SilabRAT, also known as SnappyClient, is a remote‑access trojan sold as malware‑as‑a‑service on dark‑web forums. Developed by the actor “o1oo1”, it targets financial credentials and can bypass many endpoint defenses. Defenders should harden detection, block known download points, and monitor for suspicious persistence mechanisms.
What happened
SilabRAT, also called SnappyClient, is a remote‑access trojan sold as a malware‑as‑a‑service on dark‑web forums. The threat actor “o1oo1” distributes it to steal financial credentials and has engineered it to evade many common endpoint protections.
Impact
Infected systems can silently exfiltrate credentials, install additional back‑doors, and maintain persistence through legitimate services. The RAT’s stability makes it suitable for long‑term espionage and credential‑based attacks.
Detection & Mitigation
- Block known download URLs and domains linked to the SilabRAT MaaS marketplace.
- Deploy host‑based intrusion detection rules that flag suspicious persistence mechanisms (e.g., scheduled tasks, registry run keys).
- Enable application whitelisting and restrict execution of unsigned binaries.
- Monitor for unusual outbound traffic to unfamiliar cloud or banking endpoints.
Recommended Actions
Conduct an immediate inventory of endpoints for the SnappyClient binary. Apply the latest endpoint protection signatures and enforce least‑privilege access controls. If compromise is suspected, isolate the host, perform a memory dump, and conduct a forensic analysis to confirm the presence of SilabRAT.
Related articles
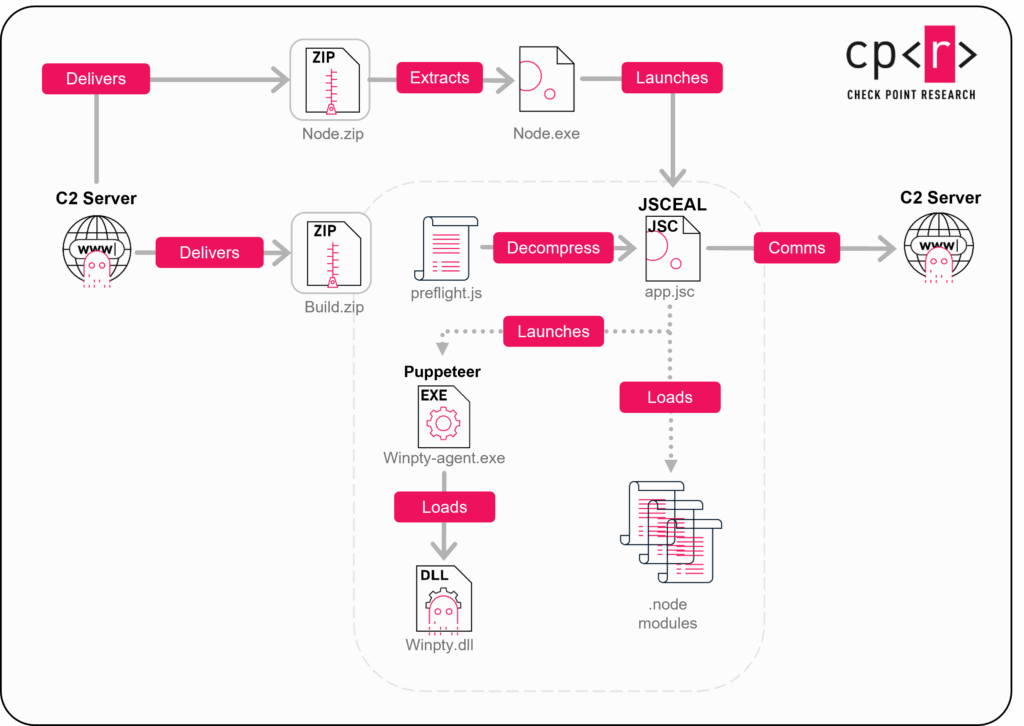
Unpacking JSCeal: Static Deobfuscation of Compiled V8 Bytecode Reveals Crypto‑Stealer Capabilities
JSCeal, a cryptocurrency‑focused stealer, arrives on victims as compiled V8 bytecode (.jsc) bundled with a Node.js runtime. Check Point Research built a fully static deobfuscation pipeline—extending the open‑source View8 decompiler—to recover pseudocode from the obfuscated, version‑specific bytecode. The recovered code exposes keylogging, credential theft, browser hijacking, and a local MITM proxy, while recent variants add extra encryption, target newer Node.js/V8 releases, and expand to macOS. The work was showcased at Black Hat USA 2026 and the deobfuscator tool is now publicly available.
Read briefing
North Korean Hackers Hijack Fake Coding Interviews with SVG Steganography to Steal Developer Credentials
A new DPRK‑aligned campaign, dubbed REF9403, injects malware into SVG flag images hidden inside seemingly legitimate coding challenge repositories. Triggered when developers run the “coding test,” the payload drops a four‑stage chain—browser credential and crypto‑wallet theft, file exfiltration, a Socket.IO RAT, and clipboard hijacking—mirroring the OTTERCOOKIE family. The attack surfaced after a Slack community received a bogus job posting and was found to be undetected by all major AV vendors. The case underscores the ongoing threat to developers and the need to scrutinize even seemingly har
Read briefing
Corporate Email Security Weaknesses Exposed: Immediate Actions for SecOps
Recent analysis shows that many organizations still rely on legacy email defenses, leaving them vulnerable to phishing, business email compromise, and credential theft. Defenders should audit current email protection, integrate threat intelligence, and deploy managed XDR to detect and block sophisticated attacks.
Read briefing
Quasar Linux RAT: Rootkit, PAM Backdoor, Credential Harvesting in Supply-Chain Threat
TrendAI uncovered Quasar Linux (QLNX), a stealthy Linux RAT that embeds a kernel rootkit, a PAM backdoor, and credential‑harvesting modules. The malware evades most AV, enabling persistent root access in compromised supply chains. Defenders should audit PAM, scan for rootkits, and enforce strict supply‑chain controls.
Read briefing