
Threat Intel
TeamPCP Container Ransomware Attack: Elastic D4C Detects Full Attack Chain
TeamPCP launched a multi‑stage container compromise that leveraged a curl‑pipe‑bash download to gain execution, established persistence, and moved laterally across Kubernetes pods. Elastic’s Defend for Containers (D4C) surfaced each phase through runtime telemetry, allowing defenders to map the chain to MITRE ATT&CK. SecOps teams should enable D4C’s pre‑built detections and monitor for the outlined indicators.
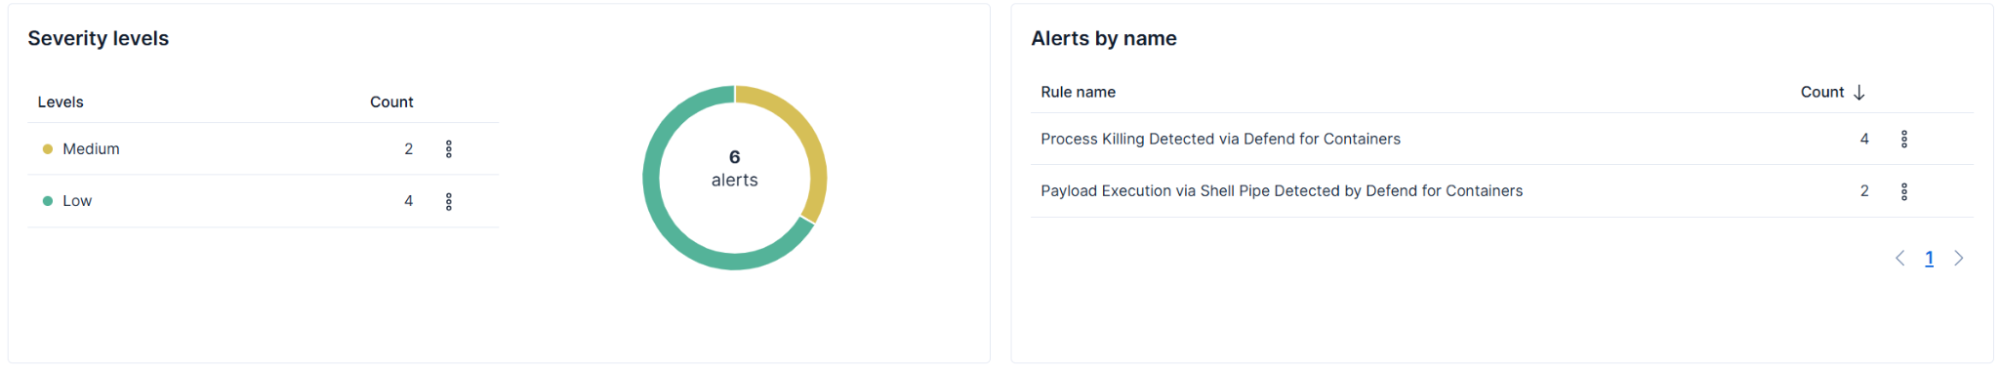
What happened
TeamPCP executed a curl‑pipe‑bash payload inside a container to download a script from 67.217.57.240:666 and run it without writing a file. The script then checked for a Kubernetes environment, established persistence, and began moving laterally across pods and nodes.
Impact
The compromise allowed the actor to prepare for large‑scale monetization, including ransomware and mining. Containers that were not isolated could be infected, leading to data exfiltration or service disruption.
Detection with D4C
Elastic’s Defend for Containers surfaced every phase of the chain through runtime telemetry. D4C’s pre‑built detections flag the curl‑pipe‑bash execution, the discovery of Kubernetes APIs, the persistence mechanisms, and the lateral movement patterns, mapping them to MITRE ATT&CK.
Mitigation steps
Enable all D4C detections and review policy rules. Block outbound traffic to unknown IPs, especially on non‑standard ports. Enforce no shell pipelines that download and execute code. Apply least‑privilege on containers and use runtime security controls to detect and stop unexpected exec calls.
Related articles
Hancitor‑Driven Cuba Ransomware: Kill Chain, TTPs, and Mitigations
Hancitor botnet is now used to deliver Cuba ransomware, exploiting Windows vulnerabilities and phishing. The attack chain includes credential theft, lateral movement, and data exfiltration. Defenders should harden endpoints, block known command‑and‑control domains, and monitor for ransomware indicators.
Read briefing
CrowdStrike Unveils Falcon Sensor Upgrade to Block Malicious Open‑Source Packages in Real Time
CrowdStrike has rolled out a new layer of protection inside its Falcon endpoint sensor that stops supply‑chain attacks before they hit the device. By using on‑device AI to classify and block malicious open‑source packages at download time, the update closes a key attack vector that has become a staple of modern ransomware and data‑exfiltration campaigns. The change is part of CrowdStrike’s broader push toward zero‑trust browser security and agentic SOC capabilities, giving defenders a faster, more autonomous shield against the ever‑evolving supply‑chain threat landscape.
Read briefing
Elastic Global Threat Report Reveals Trends and Guidance for SecOps
Elastic Security’s first Global Threat Report outlines the latest threat landscape, highlights emerging attack techniques, and offers actionable guidance for defenders. The report is built from anonymized telemetry and open detection artifacts, providing a transparent view of how Elastic’s security features perform in the field. SecOps teams can use the findings to fine‑tune detection rules, prioritize mitigations, and stay ahead of ransomware and in‑memory threats.
Read briefing
CrowdStrike Enhances Falcon with Real‑Time Supply‑Chain Defense
CrowdStrike has rolled out a new supply‑chain protection layer inside its Falcon endpoint sensor, blocking malicious open‑source packages as they download. The update expands Falcon’s threat‑intelligence reach, allowing defenders to stop supply‑chain attacks before code ever executes on the host. RootPwn breaks down how the feature works, its impact on the attack surface, and what it means for organizations still hunting for zero‑day supply‑chain exploits.
Read briefing