
Threat Intel
Trezor Warns 347,000 Users After Brevo Email Breach Sparks Phishing Campaign
Trezor revealed that a breach of its email‑service partner Brevo exposed 347,000 opt‑in newsletter addresses, which were used in a phishing attack that lured 2,500 users into clicking a malicious link. The fake “critical security alert” email claimed a microcontroller flaw in Trezor wallets could expose seed phrases. Trezor shut down the phishing domain within 20 minutes and suspended the Brevo account, stating no other Trezor systems were compromised. The incident follows earlier breaches involving Trezor’s support portal and logistics provider ShipMonk.
Trezor has confirmed that a security incident at its third‑party email provider Brevo exposed roughly 347,000 newsletter opt‑in addresses. Those credentials were immediately weaponised by threat actors who sent mass emails that mimicked Trezor’s own support team.
Phishing Campaign Details
The spoofed messages arrived from [email protected] and warned recipients of a “hardware microcontroller vulnerability” in the STM32 chips used in Trezor cold‑storage wallets. The email urged users to click a link that prompted the download of a malicious application, which then requested the wallet backup phrase.
Within 20 minutes of the first report, Trezor disabled the domain used for the phishing site, limiting the damage to about 2,500 users who had already clicked the link. The company has since suspended its Brevo account to halt further distribution.
Impact on Trezor’s Infrastructure
Trezor stresses that the Brevo breach did not affect any internal systems, wallets, or user data stored on its own servers. The only exposure was the compromised email list, which could be used for future phishing attempts.
Context: Other Recent Breaches
- January 2024: Attackers accessed Trezor’s support ticket portal, stealing data from about 66,000 users.
- Earlier this month: Hackers exploited a zero‑day SQL injection in ShipMonk’s Metabase, stealing order data for roughly 81,000 customers across several countries.
- All incidents have been isolated; no wallet seeds or private keys were compromised.
“We are actively monitoring for any signs of further malicious activity and are working closely with Brevo to secure the breach,” a Trezor spokesperson said.
Related articles
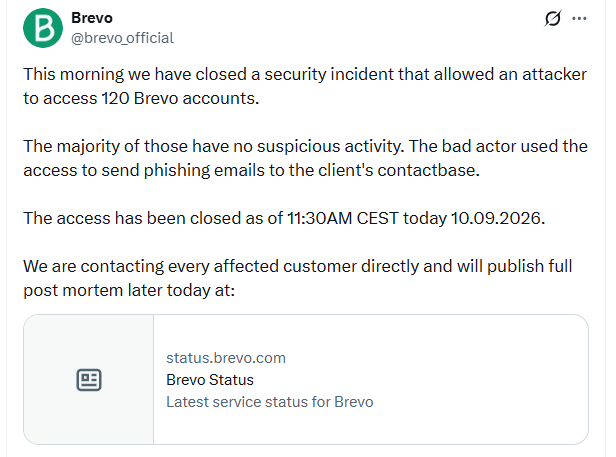
Brevo Email Platform Breach Sparks Targeted Phishing of Crypto Firms
A flaw in Brevo’s SAML SSO allowed attackers to access 138 customer accounts, some of which were used to send phishing emails to subscribers of major crypto companies. Trezor, CoinTracking, and BitBox confirmed attacks, and defenders must verify email authenticity, audit third‑party services, and monitor for abnormal activity.
Read briefing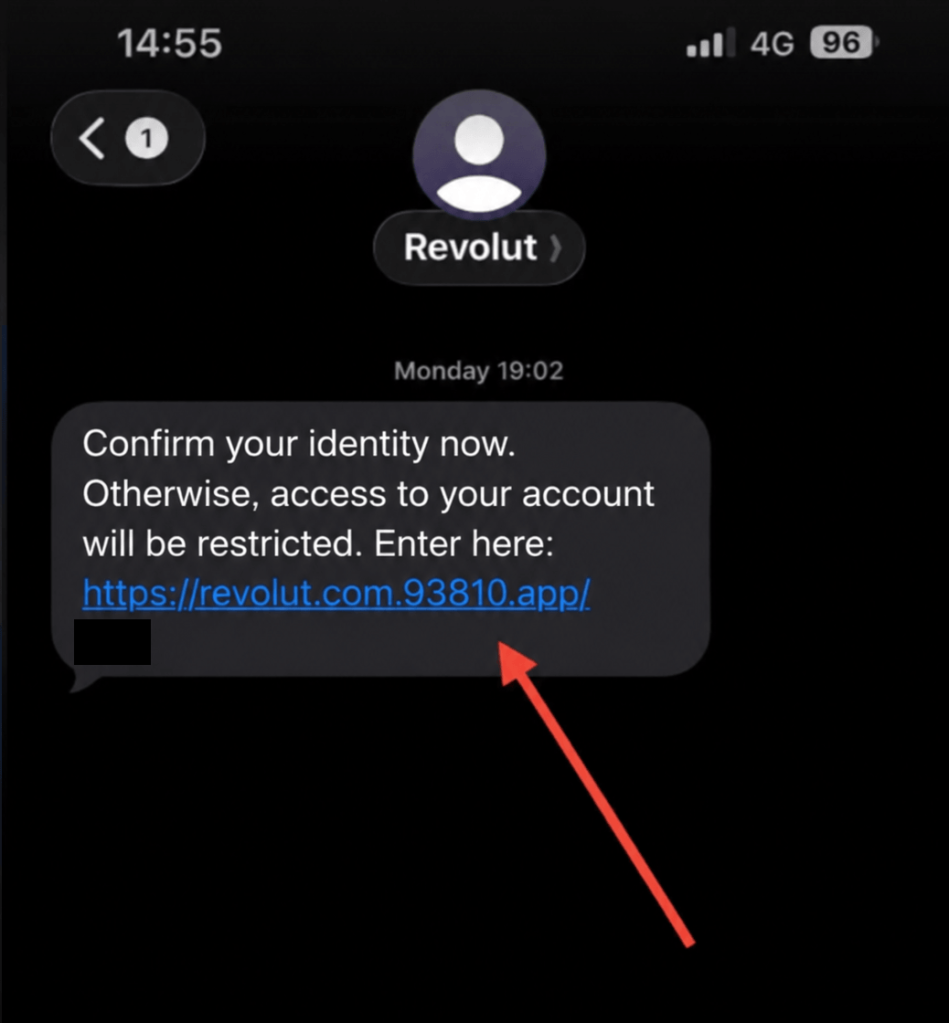
Revolut Customers Targeted by Phishing Texts After Data Breach
Revolut customers received suspicious SMS messages that appeared to come from the bank days after a breach that exposed personal and financial data. The phishing campaign mimics official alerts, requests camera access, and requests passwords, potentially enabling account takeover. Defenders should verify messages, block malicious domains, and enforce two‑factor authentication.
Read briefing
Cobalt Gang 2019 Phishing Campaign Targeting Global Financial Institutions
In 2019, the Cobalt Gang executed a sophisticated phishing operation aimed at financial institutions worldwide. The campaign leveraged spear‑phishing emails with malicious attachments to gain initial access. Defenders should review email filtering rules, enforce MFA, and conduct targeted user training.
Read briefing
ISC Stormcast: Phishing Campaign Targeting SMB Email Accounts
ISC Stormcast reports a new spear‑phishing operation delivering a remote‑access trojan to SMB email accounts. The campaign exploits attachments from seemingly legitimate vendors. Defenders should enforce MFA, update email filters, and run EDR scans.
Read briefing