
Threat Intel
Astrana Discloses SEC Filing Highlighting Social Engineering and Server Breach
Healthcare technology firm Astrana reported a data breach to the SEC after attackers used caller ID spoofing and impersonation to trick employees into granting server access. The incident resulted in the unauthorized extraction of confidential information and required systems to be restored from backups.
What Happened
Healthcare technology provider Astrana disclosed in an SEC filing that threat actors compromised its internal servers following a targeted social engineering campaign. The attackers spoofed the organization's primary corporate telephone number and impersonated internal personnel to deceive employees, ultimately securing unauthorized access to company infrastructure.
Impact
Investigation findings indicate that the intruders accessed and potentially exfiltrated confidential data residing on affected servers. Although the exact volume of impacted individuals and the specific categories of stolen information remain undisclosed, Astrana noted that the material sensitivity of the breach triggered SEC reporting requirements. Containment efforts forced the company to rebuild impacted systems using clean backups.
What to Do
Defenders and SecOps teams should review the following defensive measures to mitigate similar telephone-based social engineering vectors:
- Implement rigorous out-of-band verification workflows for any sensitive internal requests originating via voice channels.
- Enforce strict authentication and phishing-resistant multi-factor authentication (MFA) across all administrative and corporate access points.
- Monitor telephony infrastructure for anomalous inbound and outbound caller ID manipulation patterns.
- Ensure offline or immutable backup copies are maintained and regularly tested to guarantee rapid recovery without relying on compromised hypervisors or storage.
Related articles
Astrana Health Discloses Data Breach Stemming from Employee Social Engineering
Astrana Health reported a data breach impacting private and confidential records after attackers used targeted social engineering, including phone number spoofing, to impersonate internal personnel and access company servers. The healthcare management firm has enacted credential rotations, restricted remote access tools, and initiated system restorations from clean backups.
Read briefing
Inside the First Hours of a Google Workspace Breach: Live Webinar Reveals What Works and What Doesn’t
BleepingComputer partners with Material Security to host a live deep‑dive on how fast‑growing firms handle Google Workspace intrusions. The session dissects real breaches where attackers used social engineering and rogue OAuth apps, highlighting the critical early decisions that can either curb damage or amplify it. Attendees learn which controls deliver the most bang for lean security teams and hear the speakers’ take on building a resilient Workspace strategy from scratch.
Read briefing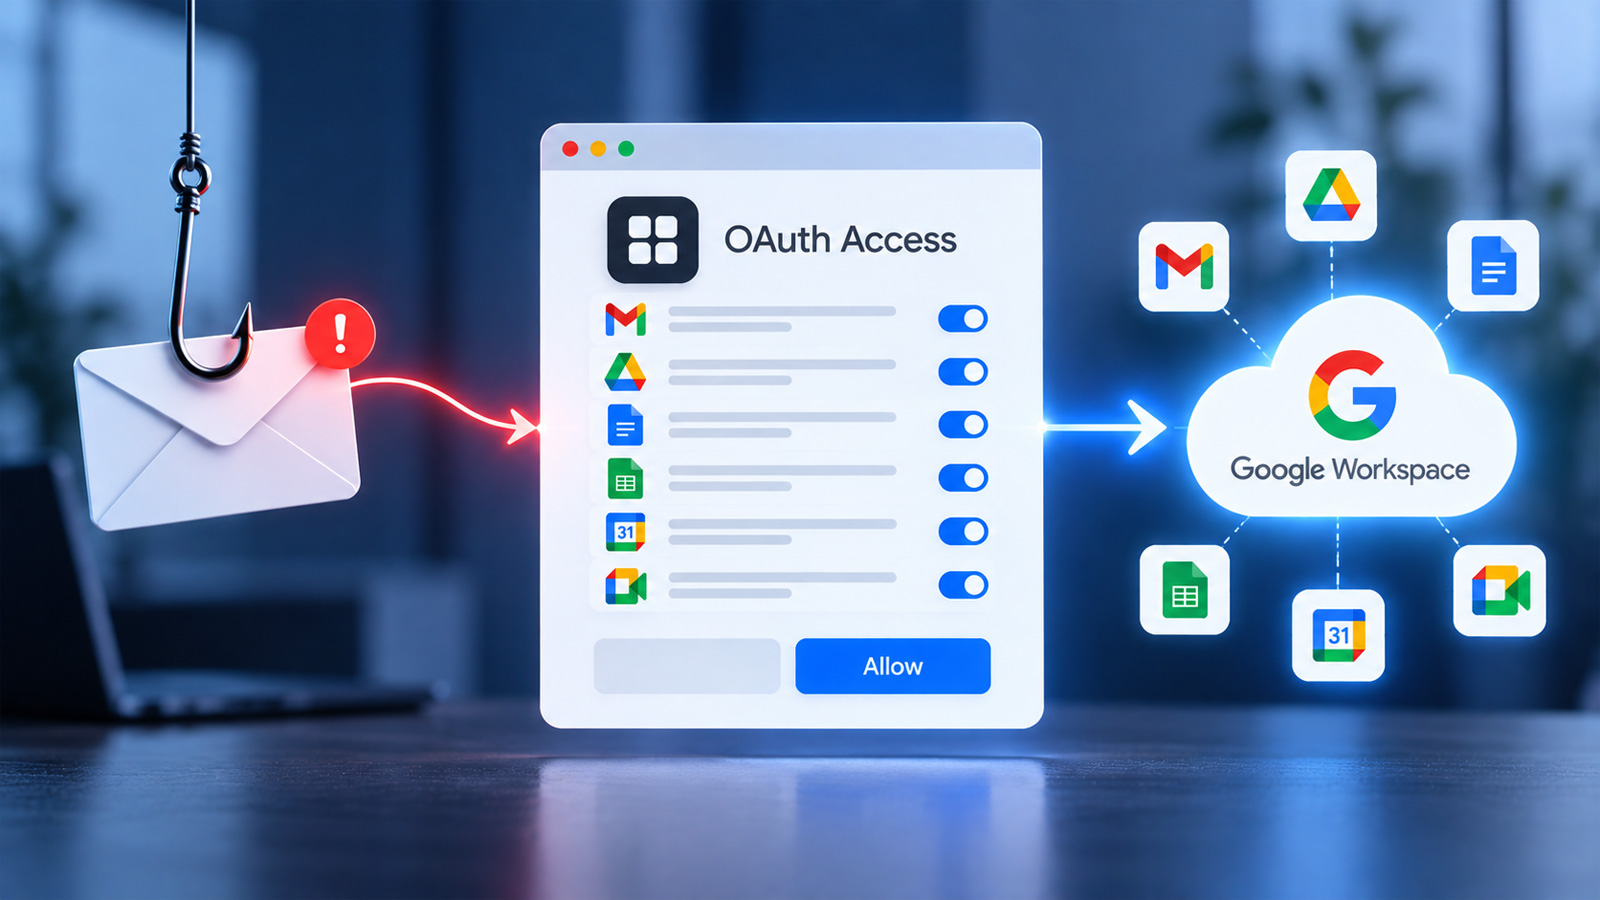
Webinar Explores How Malicious OAuth Apps Breach Google Workspace
A live session by BleepingComputer and Material Security dissected two real‑world breaches where attackers used social engineering to get users to grant permissions to rogue OAuth apps, bypassing password theft. The talk highlighted the rapid escalation of such attacks, the critical first‑hour decisions, and a prioritized list of security controls that fast‑growing firms can deploy with minimal effort.
Read briefing
Silver Fox Targets Japanese Firms with Tax and HR Phishing During Filing Season
Silver Fox is exploiting Japan’s tax filing season by sending spearphishing emails that mimic tax and HR communications. The campaign has compromised several manufacturers, highlighting the need for stricter email verification and employee awareness.
Read briefing