
Threat Intel
Fake LastPass Installers Deploy Kernel-Driver EDR Killer and Rapuncel Infostealer
A campaign using counterfeit LastPass Authenticator apps has pushed a Microsoft‑attested kernel driver that disables 145 security products and installs the Rapuncel infostealer. The attack leveraged GitHub and Cloudflare to distribute the malicious payload, impersonating at least 40 organizations. Defenders should block the malicious driver, verify kernel modules, and update EDR signatures.
What happened
A covert operation has distributed a counterfeit LastPass Authenticator via GitHub, which installs a Microsoft‑attested kernel driver that terminates 145 security products. The driver then drops the Rapuncel infostealer, which harvests credentials and sensitive data. The campaign impersonated at least 40 legitimate companies and relied on SEO and Cloudflare to surface the malicious installer.
Impact
All systems that install the driver lose protection from EDR, antivirus, and other endpoint tools, creating a blind spot for attackers. Rapuncel can exfiltrate credentials, session tokens, and other privileged information, potentially compromising corporate and personal accounts.
What to do
- Block the GitHub repositories and any URLs linked to the counterfeit installer.
- Audit kernel modules for unknown Microsoft‑attested drivers and remove any that are not signed by trusted vendors.
- Update EDR and antivirus signatures to detect the Rapuncel binary and its installation routine.
- Enforce least privilege for kernel driver installation and enable kernel integrity checks.
- Educate users to verify the source of any LastPass tools before installation.
Detection tips
Monitor for the presence of the driver’s file name and hash, watch for sudden termination of security services, and look for outbound connections to known Rapuncel command‑and‑control endpoints.
Related articles
EDR Killers: How Attackers Exploit Drivers to Disable Endpoint Detection
ESET researchers analyzed nearly 90 EDR‑killer tools used in ransomware campaigns, revealing that attackers routinely deploy vulnerable drivers or driverless tactics to suspend or block EDR software before launching encryption. The study shows driver reuse across unrelated toolsets and highlights the pitfalls of attributing attacks solely by driver signatures. Defenders should monitor driver installation, block unauthorized driver loads, and enforce EDR integrity checks.
Read briefing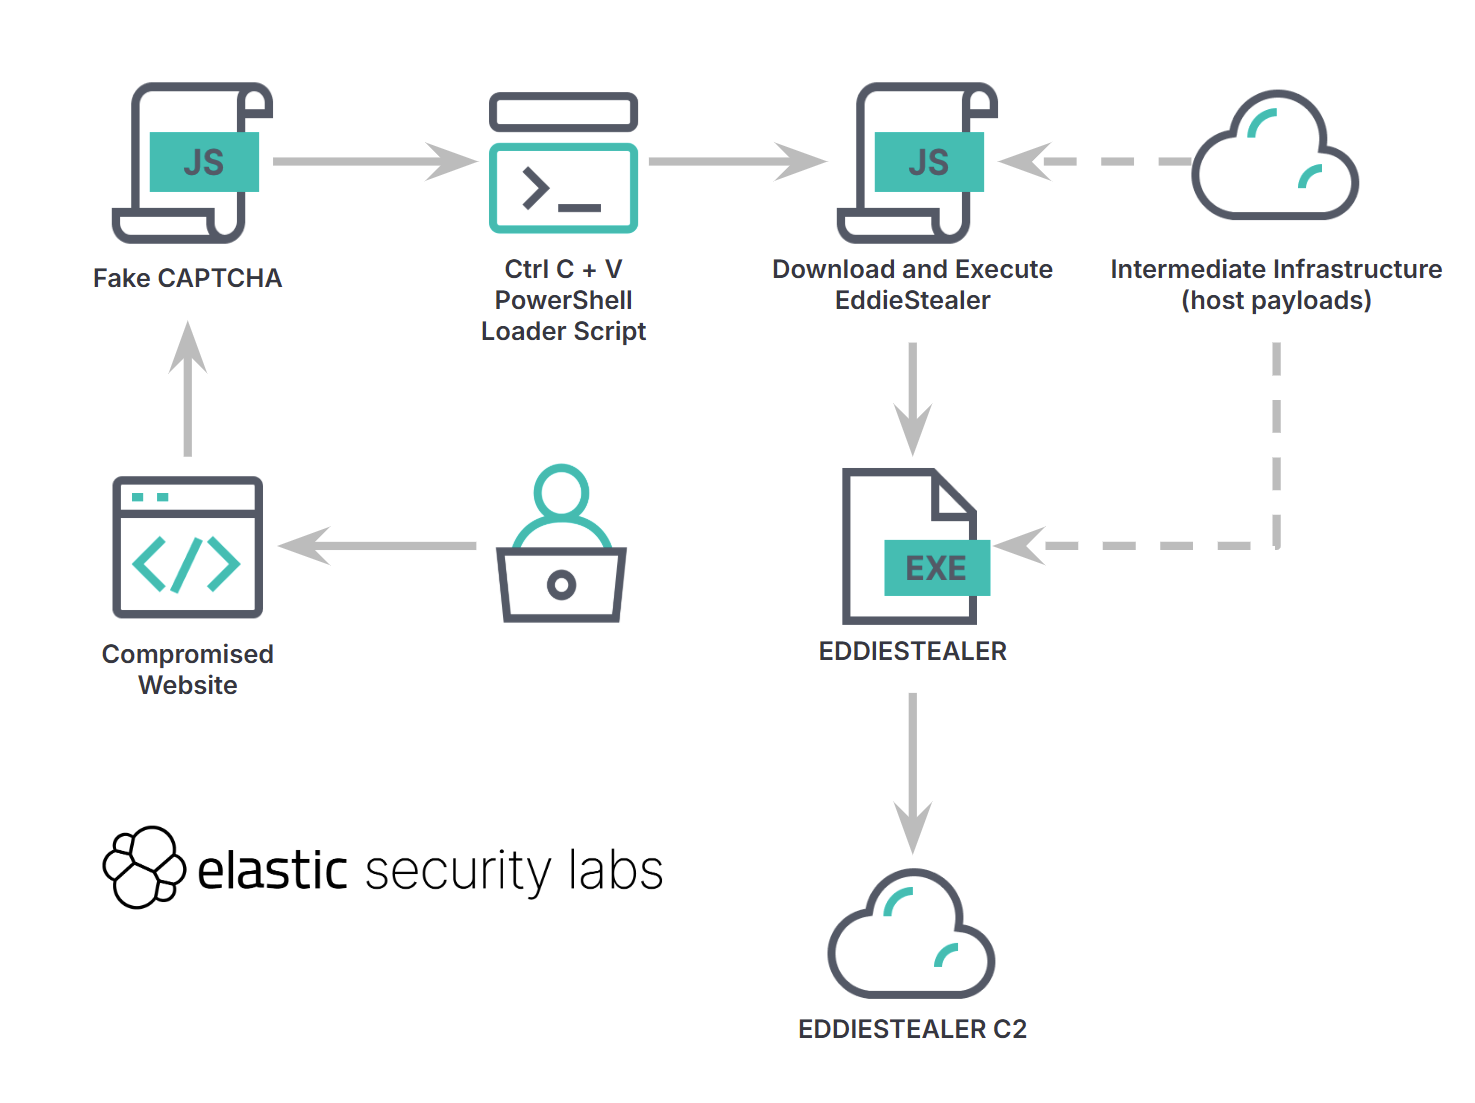
Eddiestaler: Rust‑Based Infostealer Delivered via Fake CAPTCHA Pages
A new Rust‑compiled infostealer, Eddiestaler, is being distributed through deceptive CAPTCHA interfaces that trick users into running a PowerShell payload. The malware harvests credentials, browser data, and crypto wallet info, and communicates with a C2 server for instructions. Defenders should block suspicious CAPTCHA scripts, monitor for clipboard‑copy PowerShell commands, and enforce script‑execution policies.
Read briefing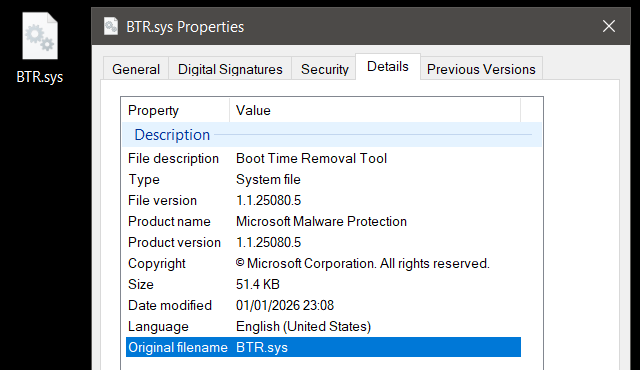
BTR Reforged: Turning a Signed Windows Defender Driver into a Kernel‑Level Attack Engine
Checkpoint Research has shown that Microsoft’s own BTR.sys – the Boot‑Time Removal driver used by Windows Defender – can be hijacked to perform arbitrary file and registry operations from Ring 0. By reverse‑engineering the driver’s encrypted transaction format and building a tool called BTR_CLI, researchers demonstrated a kernel‑mode operation primitive that bypasses EDR/AV without exploiting a vulnerability. The study exposes how trusted signed components can become powerful attack tools, urging defenders to scrutinize remediation drivers and implement stricter driver‑loading controls.
Read briefing
Warlock Attack: TightVNC, Yuze, and NSec Driver Persistence
Warlock has expanded its toolset with TightVNC, Yuze, and a BYOVD technique that loads the NSec driver, enabling persistent footholds, lateral movement, and stealth. Defenders should detect VNC usage, Yuze binaries, and the NSec driver, then apply Trend Micro updates and harden kernel driver controls.
Read briefing