
Threat Intel
MITRE ATT&CK Framework Adoption Drives Threat Intelligence Standardization
The MITRE ATT&CK® framework has become the industry standard for cataloguing adversary tactics and techniques, enabling defenders to map attacks more precisely. Security teams across sectors now use ATT&CK to structure threat intel, improve detection, and prioritize mitigations. This briefing outlines the practical steps for SecOps, sysadmins, and defenders to integrate ATT&CK into their operations.
What Happened
The MITRE ATT&CK® framework was adopted as the de‑facto reference for describing adversary behavior. It provides a comprehensive matrix of tactics and techniques that attackers use across stages of an intrusion.
Impact on Defenders
Organizations that have incorporated ATT&CK can now map indicators of compromise (IOCs) to specific techniques, improving detection coverage and response prioritization. It also facilitates sharing threat intel across teams and vendors.
What to Do
- Map existing detection rules to ATT&CK techniques to identify blind spots.
- Use the ATT&CK Navigator to visualize coverage and plan mitigation gaps.
- Integrate ATT&CK mapping into your SIEM, SOAR, and XDR platforms for automated enrichment.
- Train analysts on the ATT&CK taxonomy to improve threat hunting and incident triage.
Further Steps
Leverage Group‑IB’s Unified Risk Platform to ingest ATT&CK‑based threat intel and automate risk scoring across your environment.
Related articles
Dorothy Enables Okta Visibility Testing for SecOps Teams
Security teams can now validate their Okta SSO monitoring with Dorothy, a free open‑source tool that simulates attacker actions and maps them to MITRE ATT&CK tactics. By running Dorothy tests and leveraging Elastic Security’s detection rules, defenders can confirm that logs, alerts, and response playbooks cover the most common IAM attack vectors.
Read briefing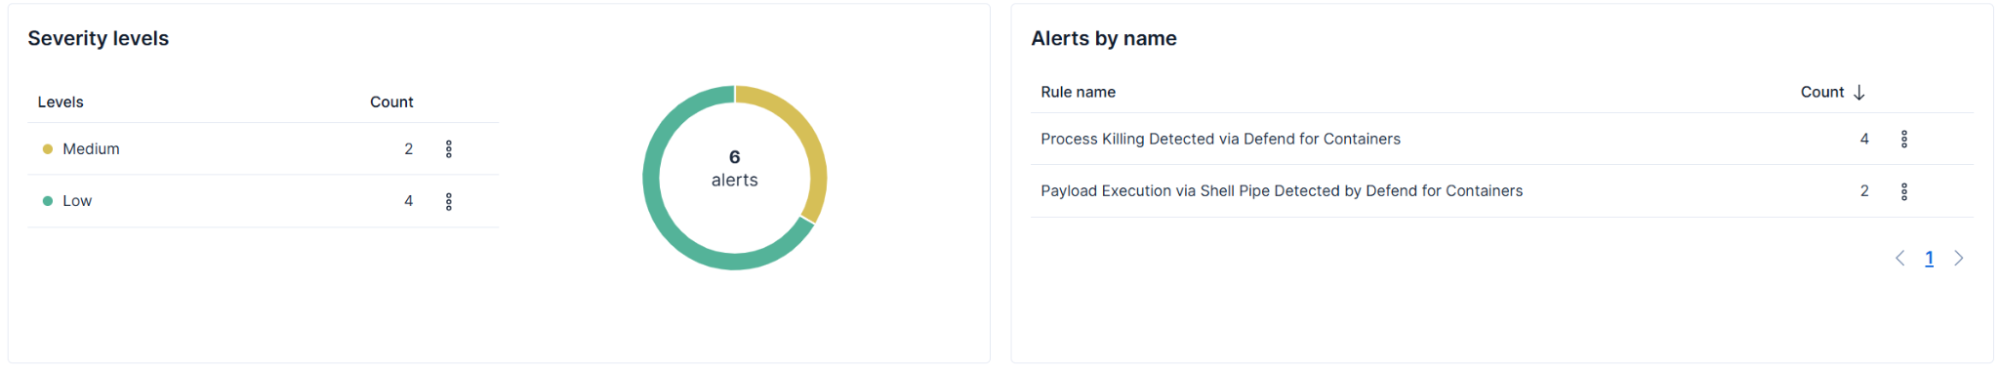
TeamPCP Container Ransomware Attack: Elastic D4C Detects Full Attack Chain
TeamPCP launched a multi‑stage container compromise that leveraged a curl‑pipe‑bash download to gain execution, established persistence, and moved laterally across Kubernetes pods. Elastic’s Defend for Containers (D4C) surfaced each phase through runtime telemetry, allowing defenders to map the chain to MITRE ATT&CK. SecOps teams should enable D4C’s pre‑built detections and monitor for the outlined indicators.
Read briefing
Elastic Releases v0.1.0 Agent Skills to Auto‑Provision Security Projects and Sample Data
Elastic has launched the first public version of its Agent Skills, letting AI coding agents create Elastic Security projects and inject realistic, ECS‑compliant sample data. Security teams can now spin up a fully populated environment from the IDE and validate detection rules against four MITRE ATT&CK‑mapped attack scenarios.
Read briefing
Fragmented Fraud Marketplaces Shift: New MITRE Framework Guides Defenders
Large fraud marketplaces have collapsed, pushing actors to niche social‑media and dark‑web shops that sell server infrastructure, targeted lists, and money‑laundering services. Security teams must broaden monitoring to these fragmented channels, ingest varied data types, and apply the new MITRE Fraud framework to prioritize detection and response.
Read briefing