
Threat Intel
Elastic Releases One‑Click Living‑off‑the‑Land Detection Package for Windows Environments
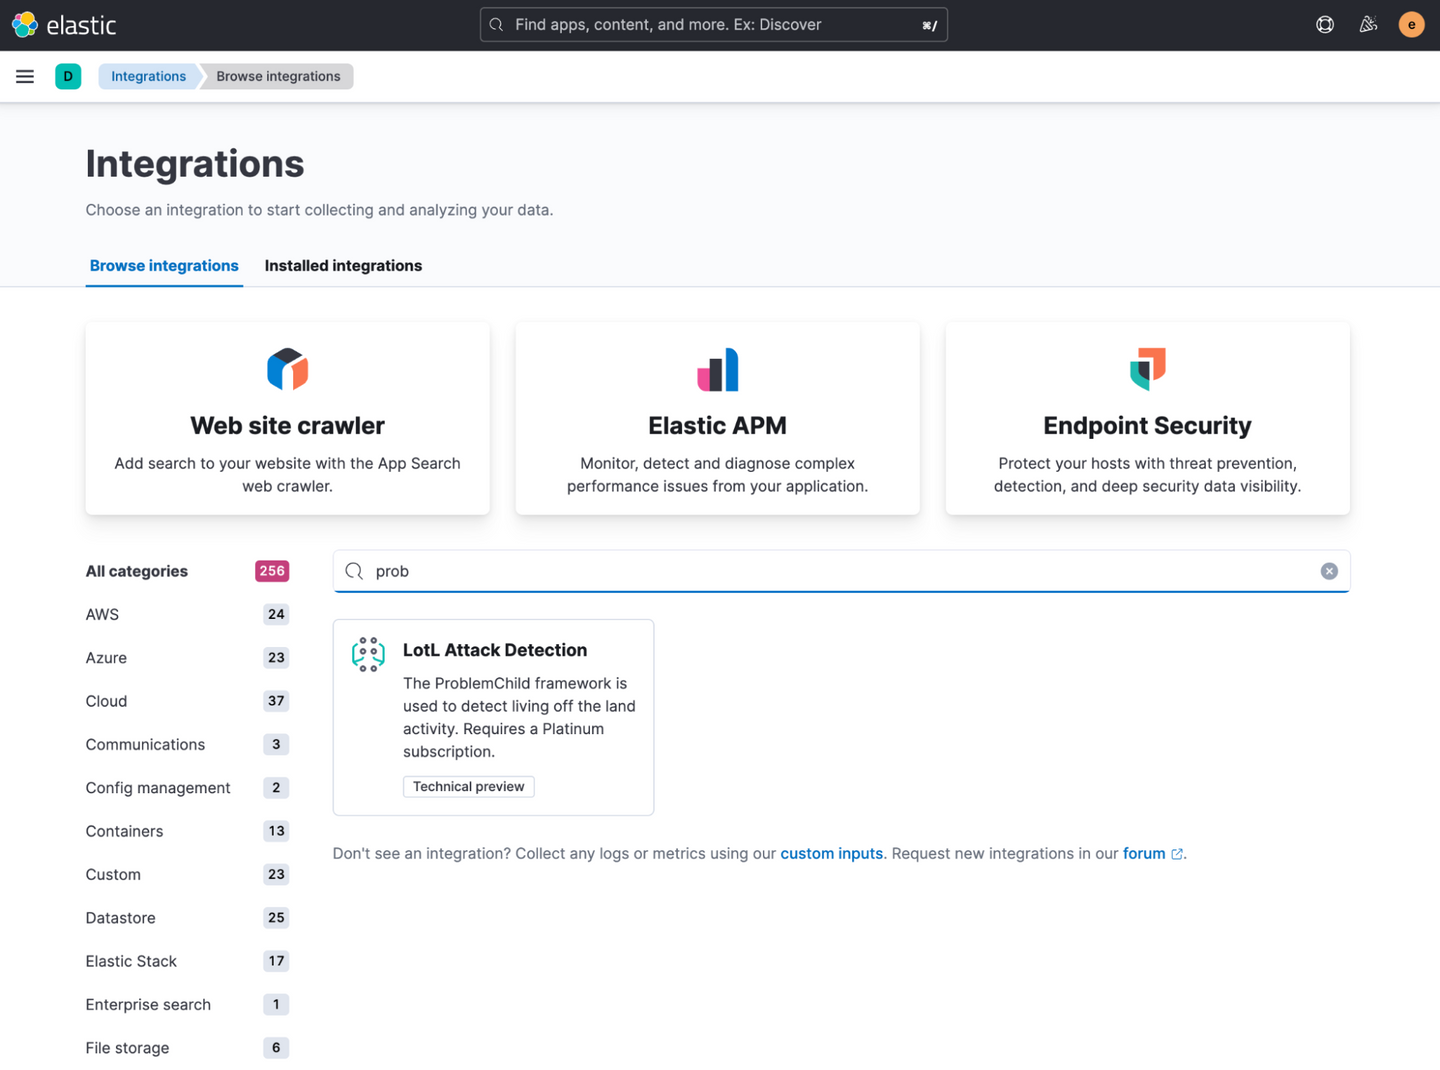
Elastic Stack now ships a pre‑configured Living‑off‑the‑Land (LotL) detection package via Kibana’s Integrations app. The package installs the ProblemChild ML model, anomaly detection jobs, and rules that flag suspicious parent‑child process chains on Windows. SecOps teams should enable the integration, verify Windows event collection, and monitor the new alerts for early LotL activity.
What Happened
Elastic added a Living‑off‑the‑Land detection package to the Kibana Integrations app. A single click installs the ProblemChild model, anomaly detection jobs, and detection rules that target Windows parent‑child process activity.
How It Works
The package uses the Process Lineage field from Windows event logs. The supervised ML model classifies each process as benign or malicious at ingest time. Anomaly detection then surfaces rare malicious processes, and rules fire on unusual parent‑child chains, indicating potential LotL attacks.
Impact
Defenders who run Windows in their environment gain an out‑of‑the‑box, end‑to‑end detection pipeline. The solution reduces manual rule creation and improves detection of stealthy, multi‑step attacks that rely on native binaries.
What to Do
- Open Kibana, navigate to Integrations, and install the “Living‑off‑the‑Land” package.
- Ensure the Windows event collector (beats/windows) is sending process events to Elasticsearch.
- Review the generated detection rules and adjust thresholds if necessary.
- Monitor the “LotL Alerts” index and investigate any high‑severity findings.
Related articles
Elastic Stack 8.3 Enables Real‑Time Command‑Line Malware Detection with Fine‑Tuned Transformers
Elastic Stack 8.3 introduced the ability to import third‑party NLP models. Security teams fine‑tuned a Hugging Face transformer for command‑line classification, achieving higher accuracy than the legacy tree‑based Living‑off‑the‑Land model while maintaining acceptable latency for real‑time SIEM pipelines.
Read briefing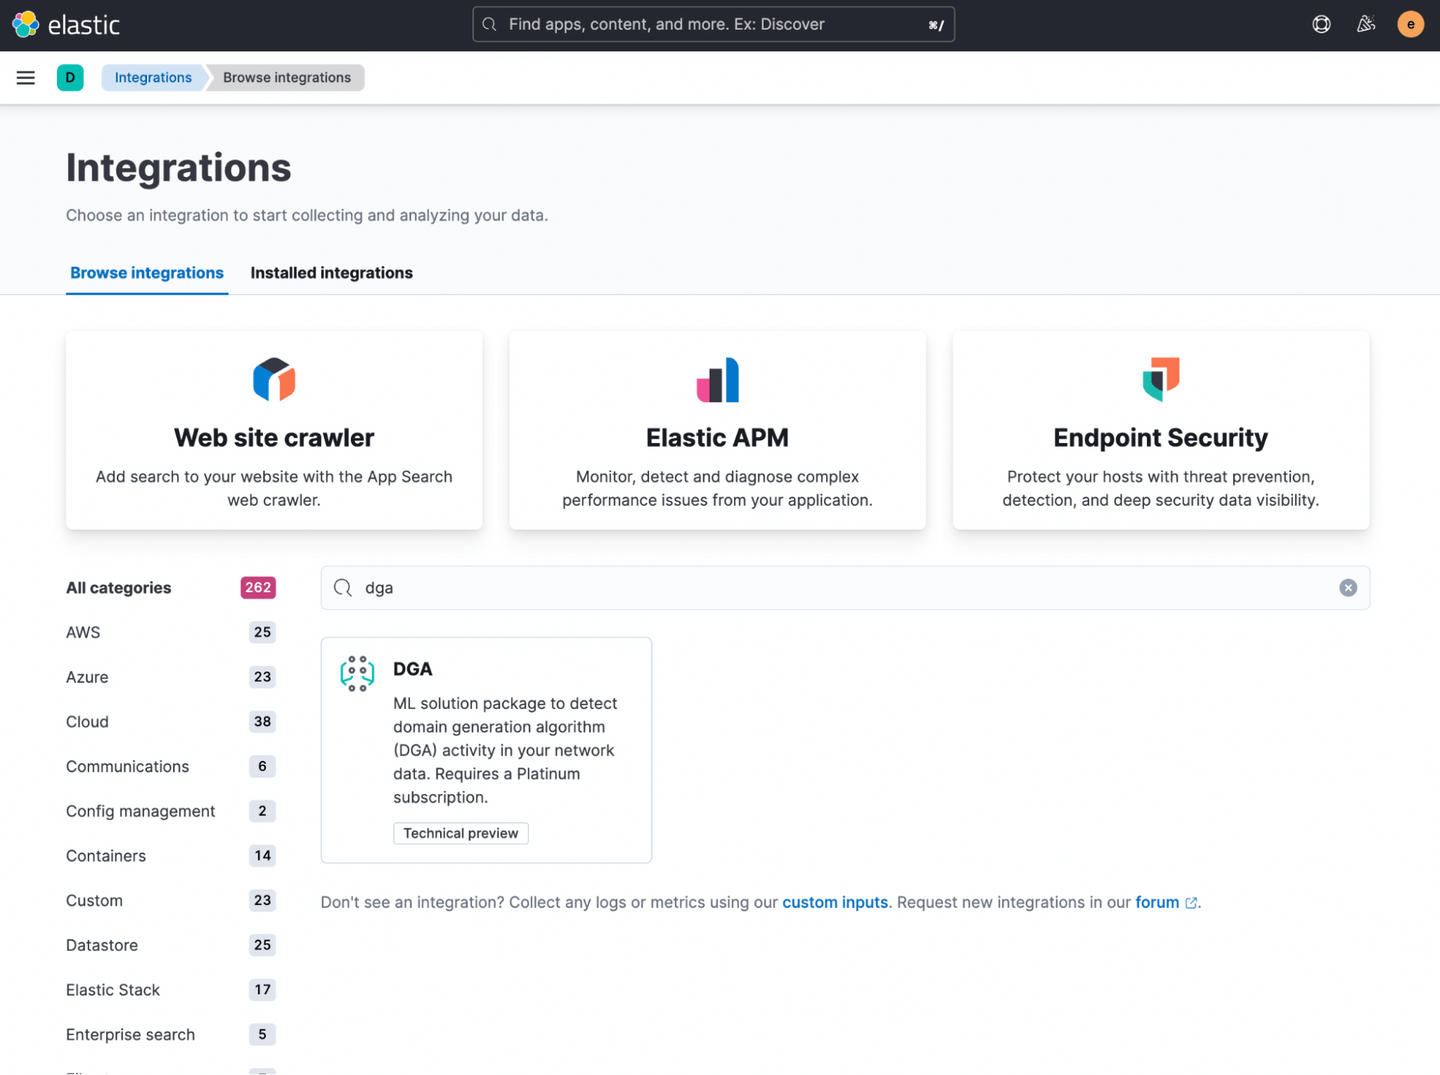
Elastic Kibana Adds One‑Click DGA Detection Package for SecOps
Elastic has released a new DGA detection package in Kibana’s Integrations app. The package installs a pre‑trained model, ingest pipelines, anomaly detection jobs, and rules in a single click, enabling defenders to spot malware using domain generation algorithms. SecOps teams should add the package, enable pipelines, and monitor alerts to block C2 traffic.
Read briefing
BlueNoroff Web3 macOS Intrusion: Attack Chain and Defenses
DPRK‑backed BlueNoroff exploited a Web3 workflow to compromise macOS endpoints. The intrusion leveraged custom malware and living‑off‑the‑land techniques. Defenders should harden Web3 integrations, monitor for suspicious binaries, and enforce strict privilege controls.
Read briefing
Detecting Hotkey‑Based Keyloggers via Undocumented Kernel Hotkey Table
Elastic Security Labs uncovered a new Windows keylogger technique that hijacks the RegisterHotKey API to capture keystrokes. The detection method uses the undocumented kernel hotkey table and ETW events from the Win32k provider, and is available in Elastic Defend 8.12.
Read briefing