
Network Security
NDR Blind Spot: Why Perimeter‑Focused Monitoring Misses Lateral Attacks
Recent analysis shows that most Network Detection and Response (NDR) solutions concentrate on perimeter traffic, leaving east‑west movement—the primary vector in modern breaches—unmonitored. Defenders must extend visibility into internal flows, integrate threat intelligence, and adopt XDR‑style correlation to detect lateral activity early.
What Happened
Network Detection and Response (NDR) deployments have traditionally been tuned to capture inbound and outbound traffic at the network perimeter. However, attackers increasingly pivot laterally within the internal fabric, exploiting internal protocols and privileged accounts. This east‑west traffic remains largely invisible to perimeter‑centric NDR, creating a blind spot that has enabled many high‑profile breaches.
Impact
Organizations with NDR focused solely on perimeter data miss the early signs of lateral movement, allowing attackers to expand footholds, exfiltrate data, or deploy ransomware before detection. The result is longer dwell times, higher data loss, and increased remediation costs.
What to Do
Defenders should immediately evaluate whether their NDR solution captures internal traffic. If not, take the following actions:
- Enable full flow capture for east‑west traffic on all internal segments.
- Integrate NDR with a SIEM or XDR platform to correlate internal flows with known malicious indicators.
- Deploy threat‑intel feeds that include lateral‑movement patterns (e.g., SMB, PowerShell, RDP, and Windows Management Instrumentation).
- Implement network segmentation and micro‑segmentation to limit lateral movement paths.
- Conduct regular internal traffic baselining and anomaly detection to spot deviations from normal patterns.
Recommendations
To close the visibility gap, consider the following best practices:
- Adopt an XDR approach that fuses NDR, endpoint detection, and threat‑intel data.
- Use automated playbooks that trigger containment actions (e.g., isolate compromised hosts) when lateral movement is detected.
- Regularly test internal traffic monitoring with red‑team or purple‑team exercises focused on lateral movement.
- Ensure that all internal protocols (SMB, LDAP, DNS, etc.) are logged and monitored for unusual activity.
Related articles
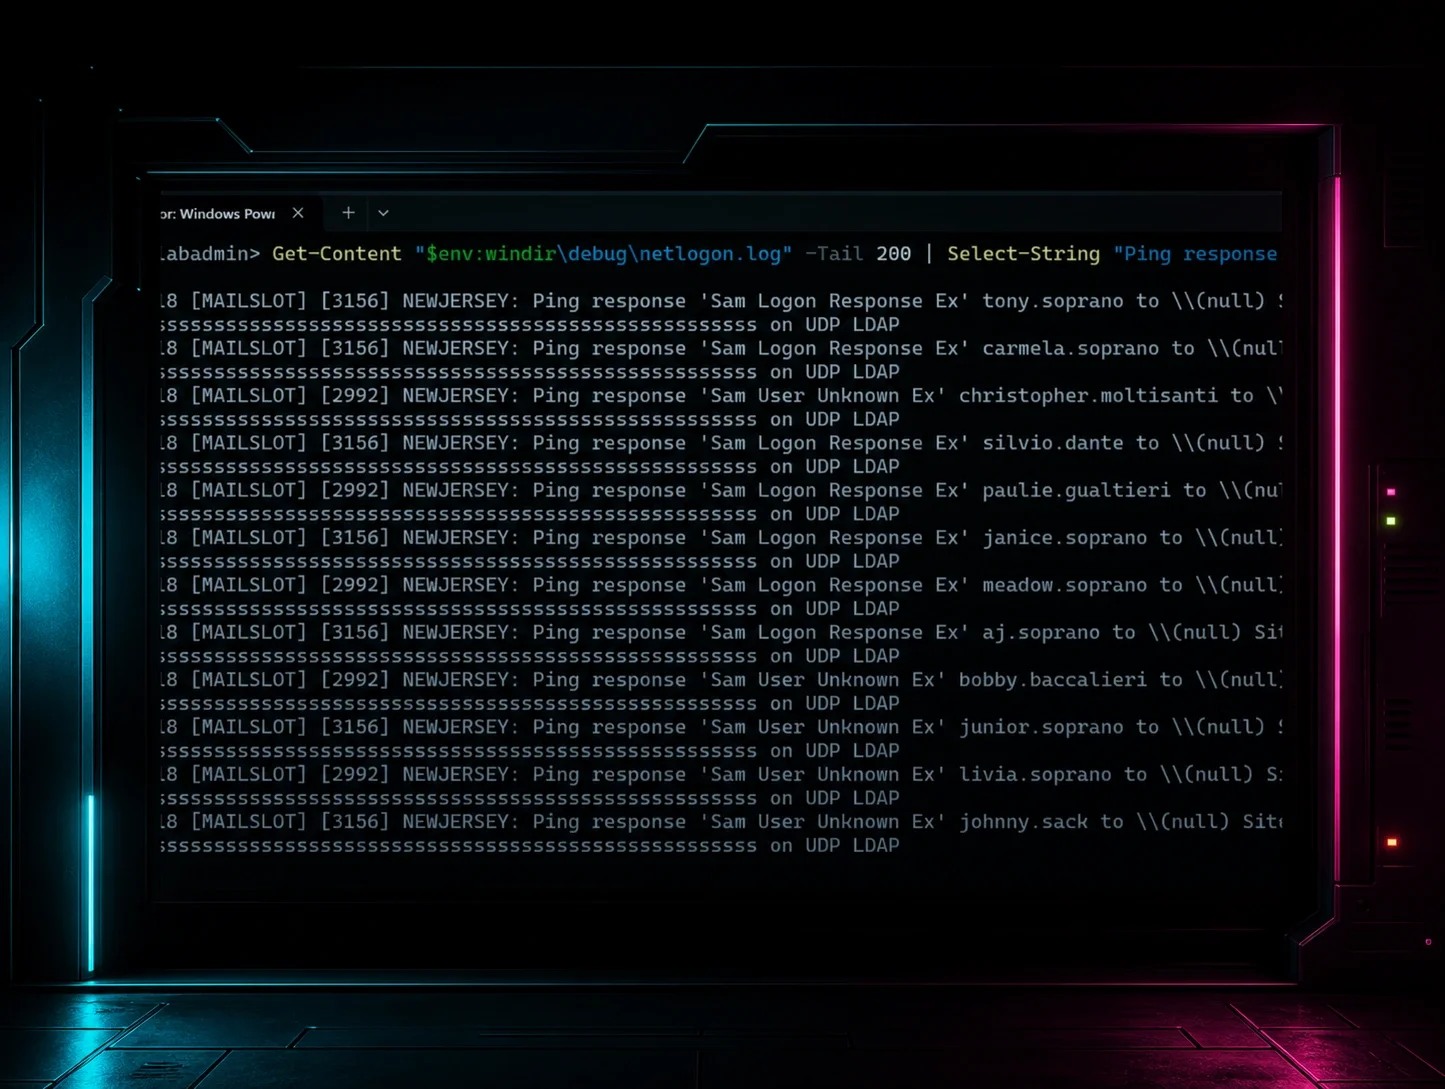
LDAP Ping Detection: Why Event 1644 Falls Short and How to Spot It
Attackers use LDAP ping for lateral movement, but Windows Event 1644 logs miss this activity. Defenders can still detect LDAP ping through netlogon.log and other audit sources. Implement targeted monitoring to close the blind spot.
Read briefing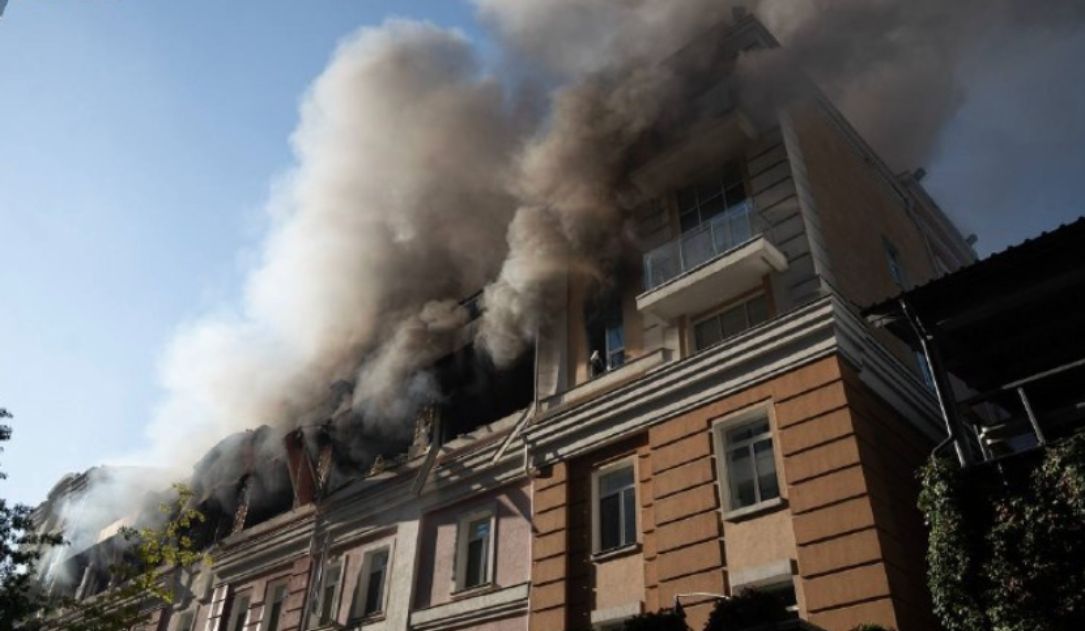
Russian Drone Strikes Damage Kyiv Data Centers and Disrupt Regional ISP Connectivity
Recent Russian drone and missile strikes targeting Kyiv damaged local data centers and telecommunications infrastructure, causing partial connectivity losses for at least four major Ukrainian internet service providers. The outages impacted approximately 100,000 households and disrupted critical civilian communications systems, prompting emergency repair operations.
Read briefing
ClickFix Attacks Exploit ClickOnce: How CrowdStrike Falcon Defends Browsers and Endpoints
ClickFix attackers force users to run malicious commands via ClickOnce, compromising browsers and endpoints. CrowdStrike’s Falcon Seraphic Enterprise Browser and platform detect and block these actions, protecting identity and SOC processes. Defenders should enable Falcon’s browser extension, update endpoint agents, and monitor for suspicious command execution.
Read briefing
Kiteworks Advises 9‑Hour System Shutdown Amid Credible Threat Intelligence
Kiteworks (formerly Accellion) has instructed customers to shut down their systems for a nine‑hour window over the weekend after receiving credible threat intelligence that a threat actor may target its platform. The advisory is preventative; no compromise evidence has been found. Defenders should apply the latest 9.5.1 patch, observe the shutdown window, and monitor for anomalous activity.
Read briefing